Configure Sophos Firewall to use DNS Protection
If you're using Sophos Firewall as a DNS server, you can configure the firewall to use DNS Protection as the DNS forwarder.
Key steps
The key steps to configure Sophos Firewall with DNS Protection are as follows:
- Turn on DNS Protection in Sophos Firewall.
- Add Sophos Firewall to a new or existing DNS Protection filtering policy in Sophos Fusion.
- Add a DNS request route in Sophos Firewall if you're using an internal DNS server to resolve local DNS requests.
- Set up network devices to use Sophos Firewall as the DNS resolver.
- (Optional) Create a NAT rule to forward outbound DNS traffic to the firewall's DNS resolver.
Set up DNS Protection
To configure the Sophos Firewall to use DNS Protection as the DNS forwarder, you must turn on DNS Protection in the firewall and then add the firewall to a DNS Protection filtering policy.
Requirements
Before you set up DNS Protection, make sure that you meet the following requirements:
- You must have a Sophos Firewall Xstream Protection subscription.
-
You must register the firewall with Sophos Fusion.
If you're using an HA cluster, make sure that you register both firewalls with Sophos Fusion.
Sophos Firewall configuration
In Sophos Firewall, do as follows:
- Go to Network > DNS.
-
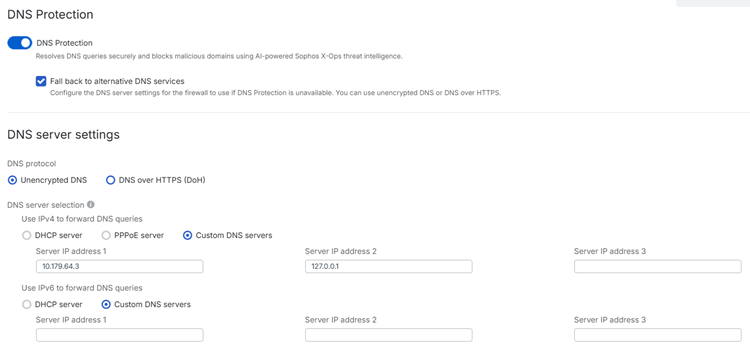
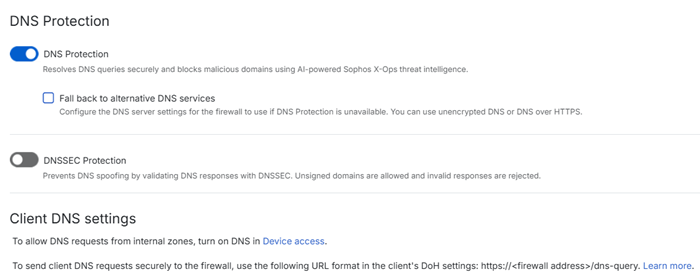
Turn on DNS Protection.
If you don't turn it on, you must configure a DNS server under DNS server settings.
-
(Optional) Select Fall back to DNS server to use a configured DNS server if DNS Protection is unreachable. If you turn this on, you must configure a DNS server under DNS server settings.
Note
If you turn on DNS Protection but don't select Fall back to DNS server, you can't configure a DNS server under DNS server settings.
Sophos Fusion configuration
In Sophos Fusion, you must add the firewall to a DNS Protection policy to apply policy-based controls on users' web browsing activities.
In Sophos Fusion, do as follows:
- Go to My Products > DNS Protection > Policies.
- Under Filtering policies, click Add policy.
-
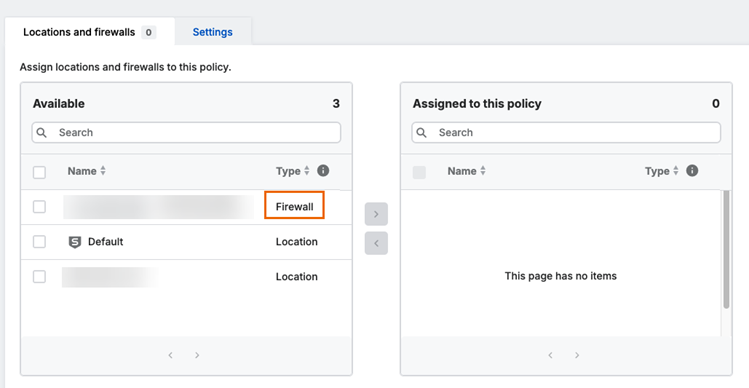
In Locations and firewalls, under Available, select the firewall and move it to Assigned to this policy.
You can identify your firewall in the Available list as follows:
-
The Name column shows a name for the firewall. It uses the following convention:
<label> <name>
- Label: It's the one you've set for your firewall in My Products > Firewall Management > Firewalls. See Add an existing firewall.
- Name: It's your firewall's serial number.
-
The Type column shows Firewall.
-
-
Click Settings to apply web access controls. See Add a filtering policy.
Migration configuration
From SFOS 23.0, Sophos Firewall supports DNS Protection over DNS over HTTPS (DoH). Sophos recommends that you migrate to the new DoH-based DNS Protection. To do so, turn on DNS Protection on the firewall. In Sophos Fusion, remove the existing location associated with the firewall from your DNS Protection policy, and then add the firewall to the policy.
After you upgrade to SFOS 23.0, do as follows:
- In Sophos Firewall, go to Network > DNS, and turn on DNS Protection.
- In Sophos Fusion, go to My Products > DNS Protection > Policies.
- Under Filtering policies, click an existing policy that includes the firewall location.
-
In Locations and firewalls, do as follows:
- Under Assigned to this policy, move the location you created for the firewall to Available.
- Under Available, select the firewall and move it to Assigned to this policy.
-
Click Save.
You can now delete the location you had created for the firewall.
Advanced Sophos Firewall configuration
In the firewall, you can add a DNS request route if you're using a local DNS server and set up your network devices to use the firewall as the DNS resolver. You can also create a NAT rule to forward all outbound DNS traffic from your internal network to the firewall's DNS resolver.
Add a DNS request route
DNS Protection doesn't resolve local DNS requests. So, if you're using an internal DNS server to resolve local DNS requests, you must add a DNS request route in the firewall.
When you add a DNS request route, the firewall resolves DNS requests as follows:
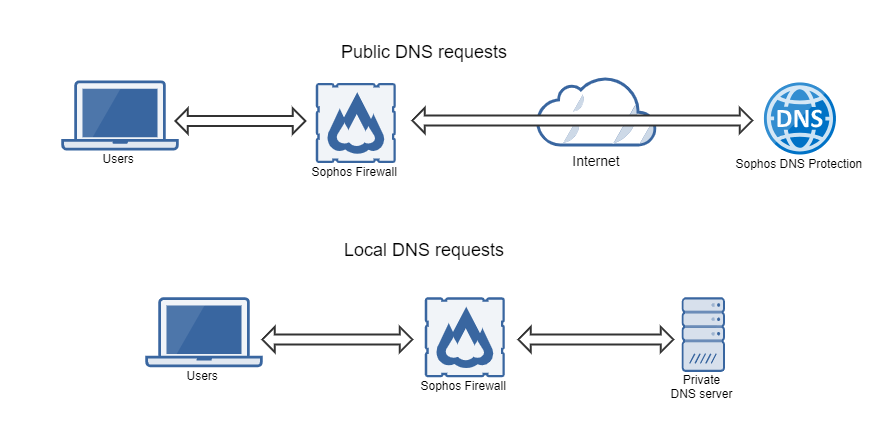
- All requests from the users go to the firewall.
- The firewall forwards local requests to an internal DNS server based on the domain.
- The firewall forwards public DNS requests to DNS Protection.
- The firewall forwards the responses from all DNS requests back to the users.
In the DNS request route, specify the local domain and internal DNS server.
To add a DNS request route, do as follows:
- Go to Network > DNS.
- Under DNS request route, click Add.
- In Host/Domain name, enter the local domain.
- In Target servers, select the internal DNS server.
- Click Save.
Set up network devices to use Sophos Firewall as the DNS resolver
Update the firewall's DHCP servers so that your network devices use the firewall as the DNS resolver.
To update the firewall's DHCP servers, do as follows:
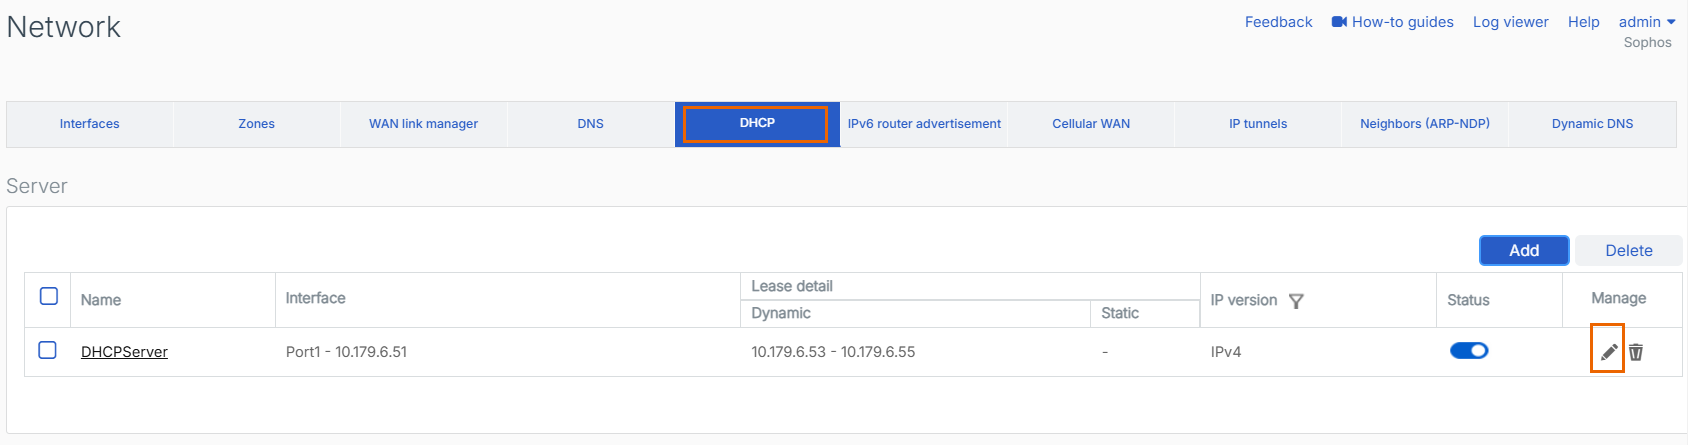
- Go to Network > DHCP.
-
Under Server, select a configured DHCP server and click Edit
 to make changes.
-
In Interface, make a note of the selected DHCP interface's IP address.
-
Under DNS server, configure the server as follows:
- Don't select Use device's DNS settings.
- In Primary DNS, enter the IP address of the DHCP interface you noted in Interface.
- In Secondary DNS, enter the public IP address of DNS Protection. This must be one of the DNS Protection IP addresses you copied from Sophos Fusion.
-
Click Save.
- Repeat these steps for all the configured DHCP servers in the firewall.
Create a NAT rule to forward outbound DNS traffic to the firewall's DNS resolver
Even after you configure all DHCP servers, some devices in your network may be configured to use a third-party DNS resolver, either through a legitimate setting or malicious one. So, you can create a NAT rule to forward all outbound DNS traffic from your internal network to the firewall's DNS resolver.
To configure a NAT rule, do as follows:
- Go to Rules and policies > NAT rules and select IPv4.
- Click Add NAT rule, then select New NAT rule.
- Enter a name for the rule and set Rule position to Top.
- In Original source, select all your internal networks.
- In Original destination, select the outboud host group. You can also select the built-in host group Internet IPv4 group instead.
- In Original service, select DNS.
- In Translated destination (DNAT), select or add the IP address of one of your firewall's internal interfaces.
-
In Inbound interface, select the firewall interfaces corresponding to the source networks you configured in Original source.
Note
Don't select the WAN port or any WAN interfaces if you have multiple WAN interfaces in the firewall.
-
Click Save.