Classic Sophos NDR on Hyper-V
Classic Sophos NDR is being replaced by Sophos NDR.
For migration options, see Migrate to Sophos NDR.
Currently, classic Sophos NDR supports Microsoft Hyper-V 6.0.6001.18016 (Windows Server 2016) or later.
The main steps are as follows:
- Check the requirements below.
- Configure an integration. This configures an image to use on a VM.
- Configure your switches so NDR can see traffic.
- Download and deploy the image on your VM. This becomes the appliance.
Requirements
- Currently, Sophos supports Microsoft Hyper-V 6.0.6001.18016 (Windows Server 2016) or later.
- The VM that runs the appliance must meet general system, processor, and network access requirements. See Minimum system requirements and CPU requirements.
- For a quick guide on resizing the VM for optimal performance, see Classic Sophos NDR VM appliance size guide.
Note
We don't support Processor Compatibility Mode.
Configure an integration
To configure the integration, do as follows:
- Sign in to Sophos Fusion as an Admin or Super Admin.
- Go to Security Operations > Integrations > Marketplace.
- Click Sophos NDR.
- Click Continue to be redirected to the classic Threat Analysis Center, where configuration takes place.
-
On the NDR page, in Data Ingest (Security Alerts), click Add Configuration.
Integration setup steps appears.
Configure the VM
-
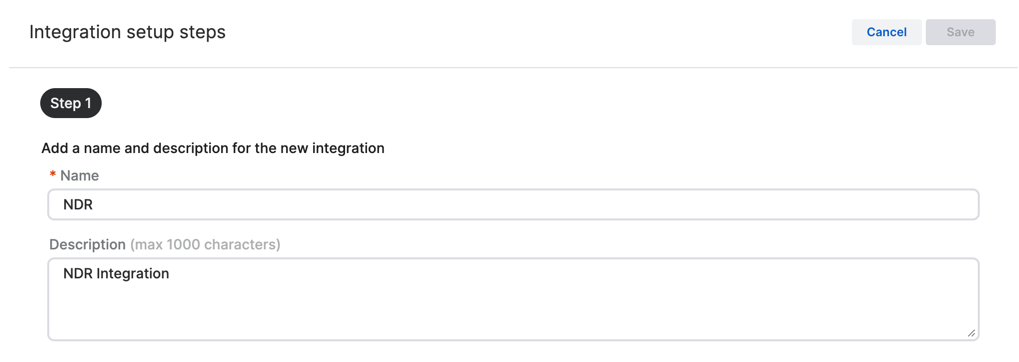
In Step 1, enter a name and description for the integration.
-
In Step 2, select or create the appliance that will collect NDR logs.
You can only have one NDR integration per appliance.
If you need a new appliance, click Create new appliance and follow the instructions in the next step.
If you want to use an existing appliance, select it from the drop-down list and skip to Step 3 to set exclusions.
-
To create a new appliance, do as follows:
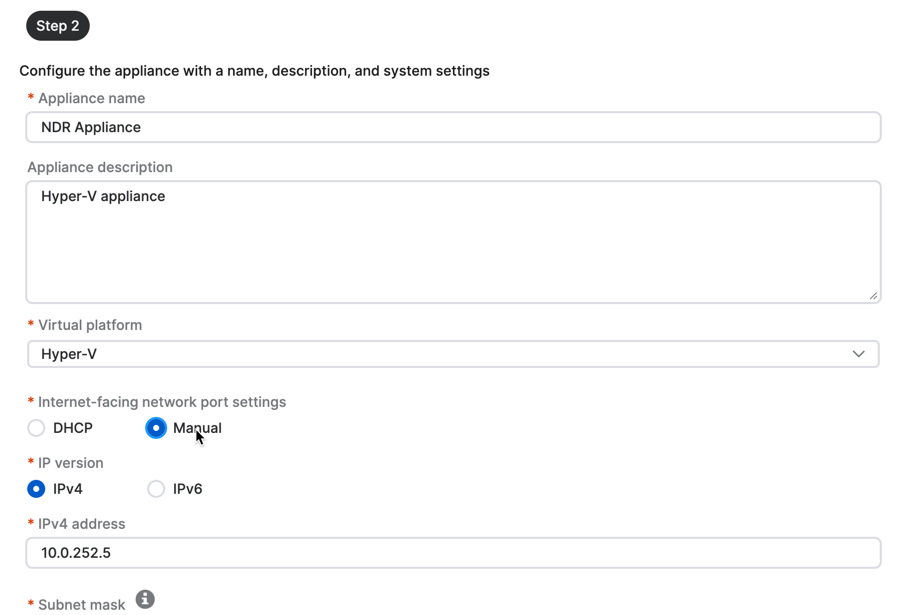
- Enter the appliance name and description. You must enter a unique name.
- Select the virtual platform (Hyper-V).
-
Specify the internet-facing network ports.
-
Select DHCP to assign the IP address automatically.
Note
If you select DHCP, you must reserve the IP address.
-
Select Manual to specify network settings.
Example
- IP address: 10.0.252.5
- Subnet mask: 255.255.255.0
- Gateway address: 10.0.252.1
- DNS 1: 8.8.8.8
- DNS 2: 8.8.4.4
-
-
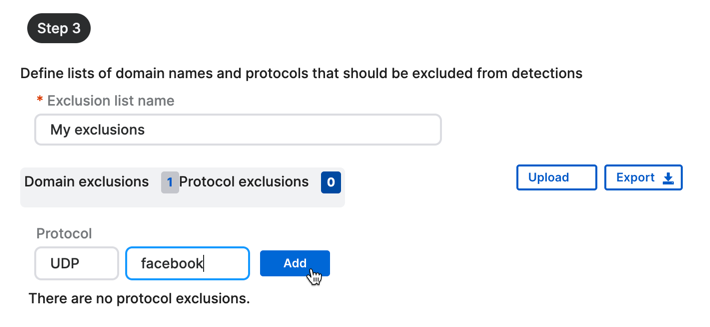
In Step 3, exclude specific domains and protocols from checking. For example, you might do this if you have a domain that causes false positives.
You can set up your exclusions later, but you must enter an exclusion list name now.
- Enter an Exclusion list name.
- To exclude a domain, click Domain exclusions. Enter the domain name, for example,
sophos.com, and click Add. -
To exclude a protocol, click Protocol exclusions. You can enter information in either or both of the fields:
- In the first field, enter a master protocol. For example,
TCPorUDP. - In the second field, enter a sub-protocol (website). For example,
facebook.
If you enter information in both fields, we assemble them into one string with a single dot separator.
We don't recommend excluding a master protocol completely. Only do this if a high-traffic protocol that isn't usually risky, like a routing protocol, generates too much data.
- In the first field, enter a master protocol. For example,
-
Click Add.
You can export your exclusions as a JSON file. You can also upload exclusions to the list from a previously exported JSON file.
-
Scroll back to the top and click Save.
-
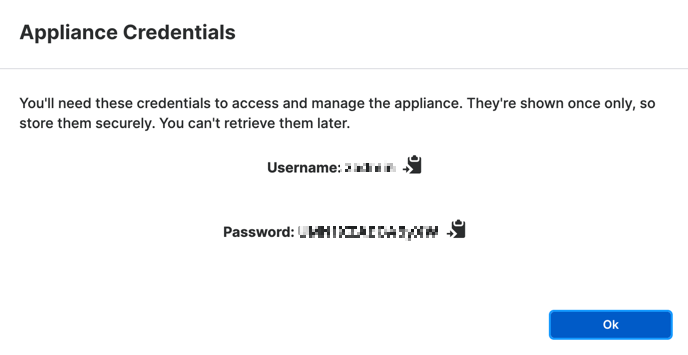
The username and password for your appliance are shown on the next screen. It's very important that you note these down immediately, as they won't be shown again, and you need them to access and manage the appliance.
Click OK once you've saved them.
On the NDR page, you see the new integration in the list of configured integrations.
Next, configure your switches so the NDR appliance can monitor your network traffic.
Configure your switches
Before you download and deploy the classic Sophos NDR VM, you must set up port mirroring, also known as Switched Port Analyzer (SPAN). This forwards a copy of incoming and outgoing traffic from a switch's ports or VLANs to another switch port for analysis.
You must configure port mirroring for both virtual internal and physical external network traffic.
When you deploy your NDR VM appliance later, you’ll be able to connect it to your SPAN ports so that NDR can monitor network traffic.
Port mirroring involves the following steps:
- Configure a traffic mirroring port with Hyper-V.
- Attach a SPAN Virtual Interface to the virtual switch.
- Turn on Microsoft NDIS capture extensions.
- Configure the switch's mirroring mode.
- Validate traffic mirroring.
For instructions, see Configure traffic mirroring with a Hyper-V vSwitch.
Next, you download the NDR VM image.
Download the VM image
Now you download the NDR image you need to deploy and boot the new VM.
-
Next to the new integration, click the three dots in the Actions column, and click Download image.
You see the download start.
-
Hover over the icon to the left of the integration name. You now see "Waiting for deployment".
You're ready to deploy the VM.
Deploy the VM
The ZIP file you downloaded in Sophos Fusion contains the files you need to deploy your VM: virtual drives, seed.iso, and a Powershell script.
Note
Don't add more than 32 GB of RAM and 8 CPU cores to a Hyper-V virtual machine. Exceeding these limits may result in more than one Non-Uniform Memory Access (NUMA) node per CPU socket, which NDR doesn't support. NDR supports only one NUMA node and one CPU socket.
To deploy the VM, do as follows:
- Extract the ZIP file to a folder on your hard drive.
- Go to the folder, right-click the
ndr-sensor.ps1file, and select Run with PowerShell. -
If you see a Security Warning message, click Open to allow the file to run.
You're prompted to answer a series of questions.
-
Give the VM a name.
- The script shows the folder where the VM files will be stored. This is a new folder in your default installation location for virtual drives. Enter
Cto allow the script to create it. - Enter the number of processors (CPUs) to use for the VM.
- Enter the amount of memory to use in GB.
-
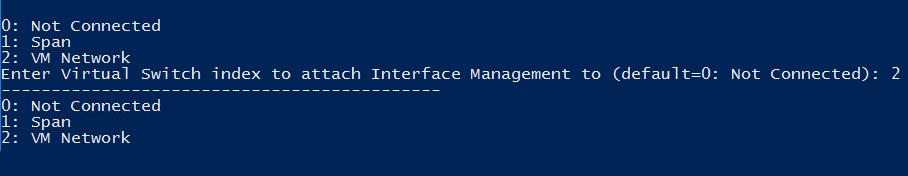
The script shows a numbered list of all your current vSwitches.
Select the vSwitch you want to attach the management interface to and enter its number. This interface lets the appliance send data to the Sophos Data Lake.
You set up this interface earlier in Sophos Fusion in Internet-facing network port settings.
If you selected DHCP during setup, make sure the VM can get an IP address via DHCP.
-
You don't need to enter a vSwitch for the syslog interface. This is only relevant for third-party product integrations.
Select any vSwitch as a placeholder and disconnect it in the VM settings later.
-
Select the vSwitch that will receive SPAN traffic for the NDR application. You configured this earlier. See Configure your switches.
-
Optionally, select a second vSwitch that will receive SPAN traffic and needs monitoring (if you have one). For example, you might have a physical switch and a vSwitch that doesn't send traffic to the physical switch.
If you use a second vSwitch, you must increase the number of CPUs for the VM to at least 8. See Classic Sophos NDR VM appliance size guide.
-
The PowerShell script sets up the VM in Hyper-V. You'll see an Installation Completed Successfully message.
- Use any key to exit.
-
Open the Hyper-V Manager to see the VM added to the list of virtual machines. If you need to change any settings, you can. Then power it on.
The VM boots for the first time and checks that it can connect to the correct vSwitches and the internet. Then it reboots. This can take up to 10 minutes.
-
In Sophos Fusion, go to the Integrations page for the product you're integrating and refresh it. The VM's status is now Connected.