Investigation Console
The NDR investigation console is a virtual machine that receives flow data from your NDR appliances. You can use this data for threat hunting.
Note
The investigation console supports Sophos NDR and classic Sophos NDR.
You create an investigation console in Sophos Fusion but run it on your local network. The investigation console gets data from the NDR appliances you add to it and lets you monitor or query it.
To see the Investigation Console page in Sophos Fusion, go to My Products > NDR. Under Investigate, select Investigation Console.
Create an investigation console
Before you create an investigation console, you must deploy an NDR appliance. See Deploy Sophos NDR.
The key steps in creating an investigation console are as follows:
- Configure an investigation console. This creates an image you'll deploy on your virtual network.
- Download the image and deploy it.
- Add an NDR appliance to the investigation console. This sends NDR data to the investigation console.
Configure an investigation console
- Go to My Products > NDR > Investigation Console.
-
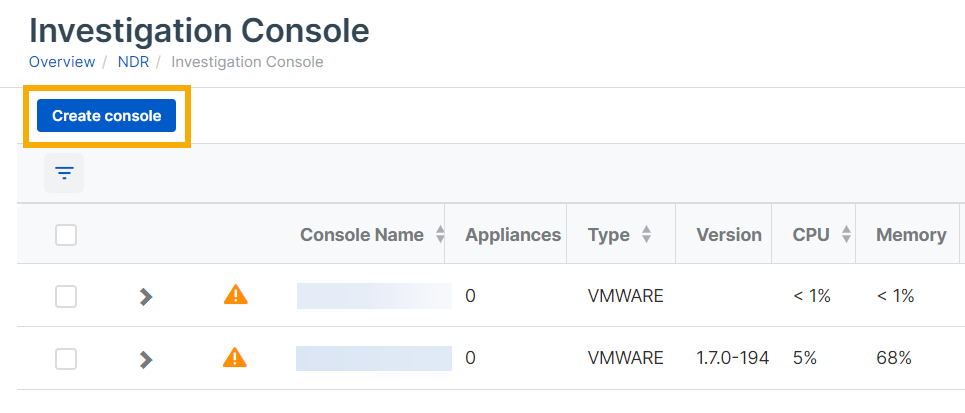
Click Create console.
-
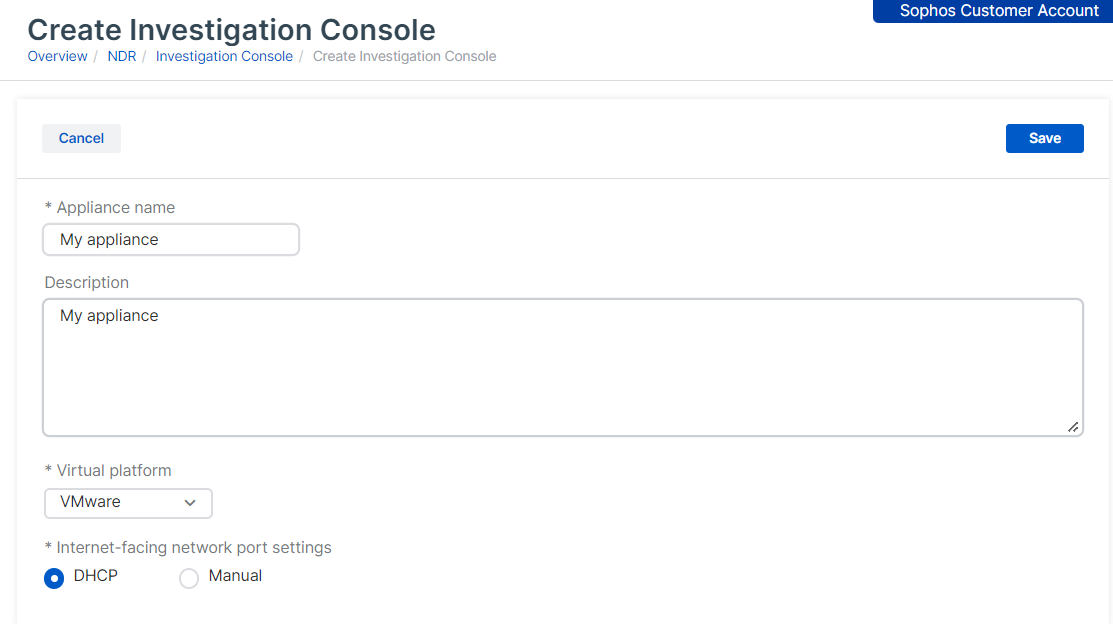
Configure the investigation console as follows:
- Enter a Name and Description.
- Select the Virtual platform, either VMware or Hyper-V.
- The Hostname defaults to
ndr-investigation-consoleand can't be changed later. -
The Network Port defaults to
4000.NDR appliances connect to the investigation console on this port. You must allow traffic on this port from the assigned appliances to the investigation console.
-
Specify the Internet-facing network port settings. This sets up the management interface.
This is the investigation console's only network interface. The investigation console uses it to communicate with Sophos Fusion and its assigned NDR appliances.
-
Select DHCP to assign the IP address automatically.
Note
If you select DHCP, you must reserve the IP address.
-
Select Manual to specify network settings. All fields except DNS 2 are required.
-
-
Click Save.
-
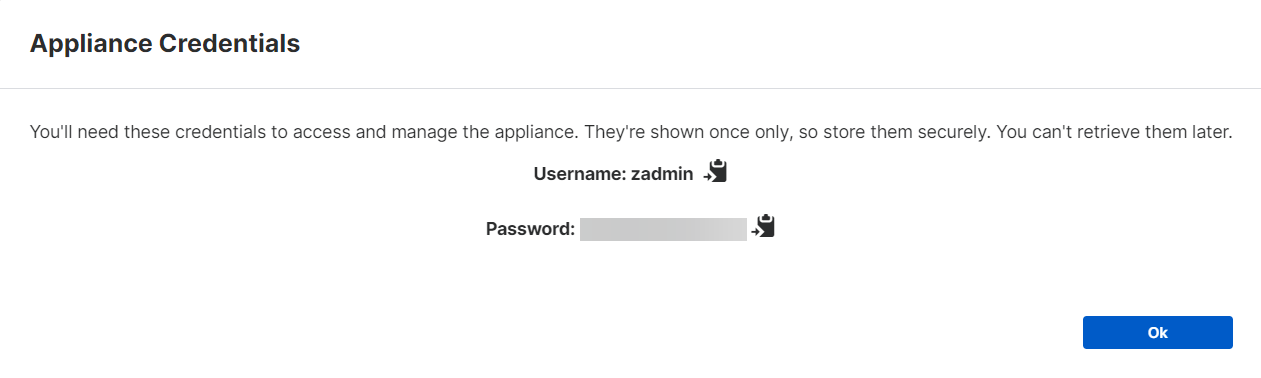
An Appliance Credentials pop-up shows the credentials for accessing the investigation console VM.
The username is
zadminand the password is shown in the message. Store the password safely. It's only shown once.Click Ok.
-
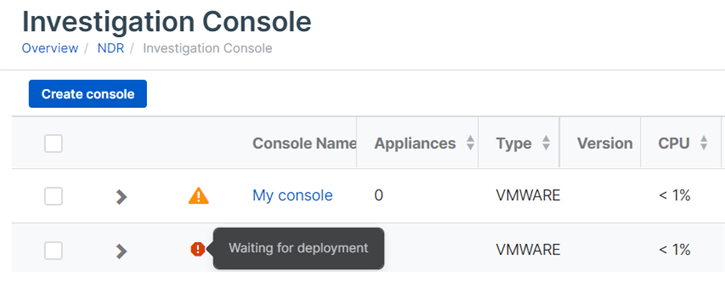
On the Investigation Console page, the new investigation console is shown in the list with a red warning icon
 .
The image can take up to five minutes to be created.
-
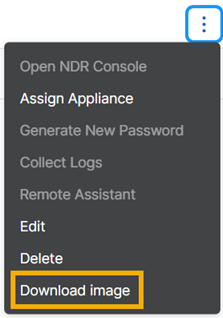
Click the three dots on the right of a row and select Download image.
Deploy the image
Deploy the image in your environment.
Deployment depends on whether you're using VMware ESXi or Hyper-V. Select the tab for your virtual platform.
Restriction
Each downloaded OVA file can be used to deploy one investigation console. To deploy another investigation console, create it in Sophos Fusion and download its OVA file.
On your ESXi host, do as follows:
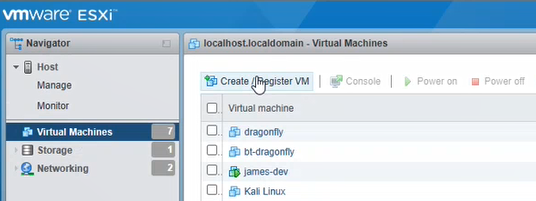
- Select Virtual Machines.
-
Click Create/Register VM.
-
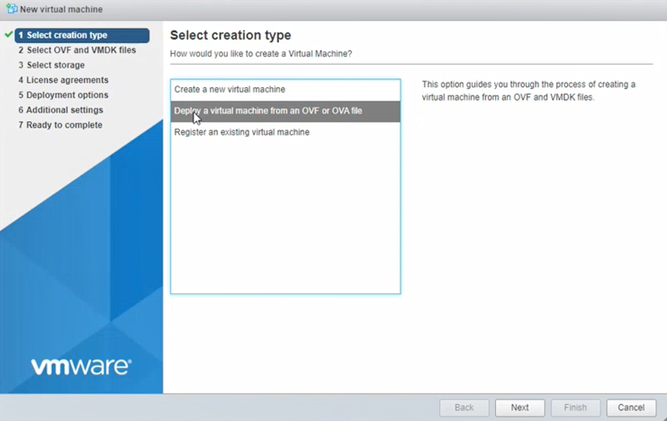
In Select creation type, select Deploy a virtual machine from an OVF or OVA file. Click Next.
-
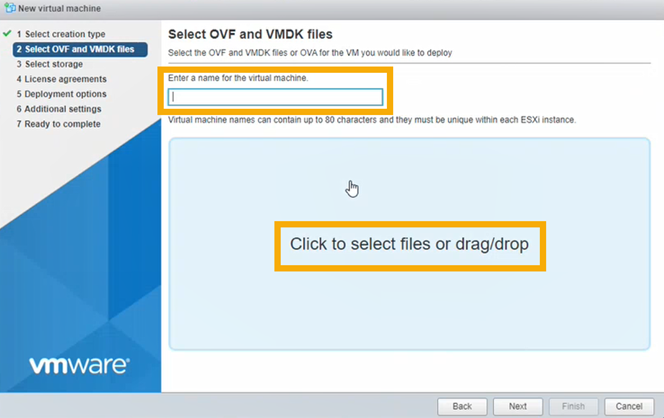
In Select OVF and VMDK files, do as follows:
- Enter the VM name.
- Upload the OVA file you downloaded in Sophos Fusion.
- Click Next.
-
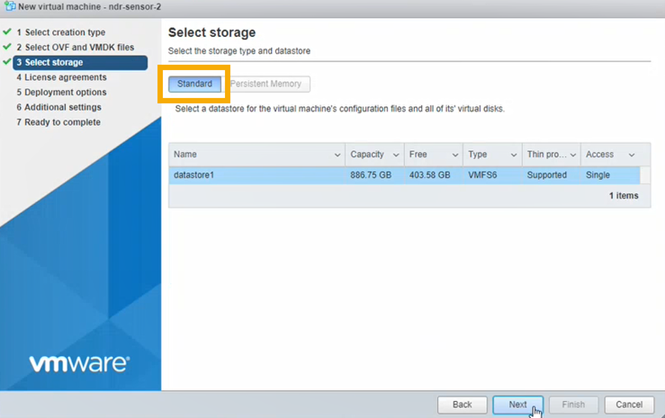
In Select storage, select Standard storage.
Select the datastore where you want to put your VM, then click Next.
-
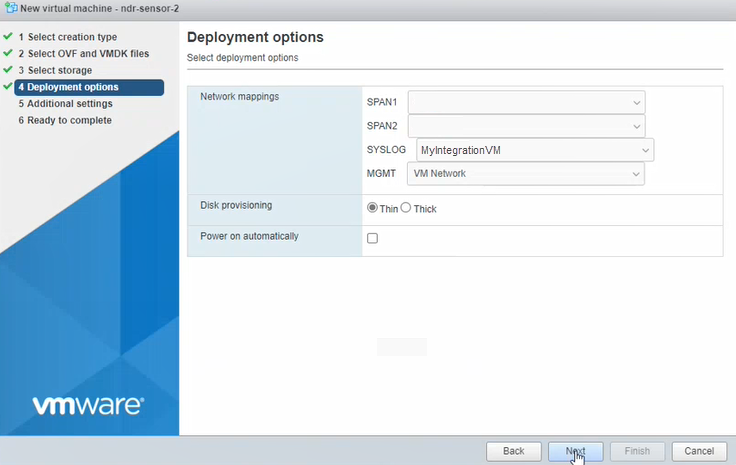
In Deployment options, enter the settings as follows:
-
In MGMT, select the management interface for the appliance.
You set up this interface earlier in Sophos Fusion in Internet-facing network port settings.
If you selected DHCP during setup, make sure the VM can get an IP address via DHCP.
-
In Disk Provisioning, make sure Thin is selected.
- Make sure Power on automatically is selected.
- Click Next.
-
-
Skip the Additional settings step.
-
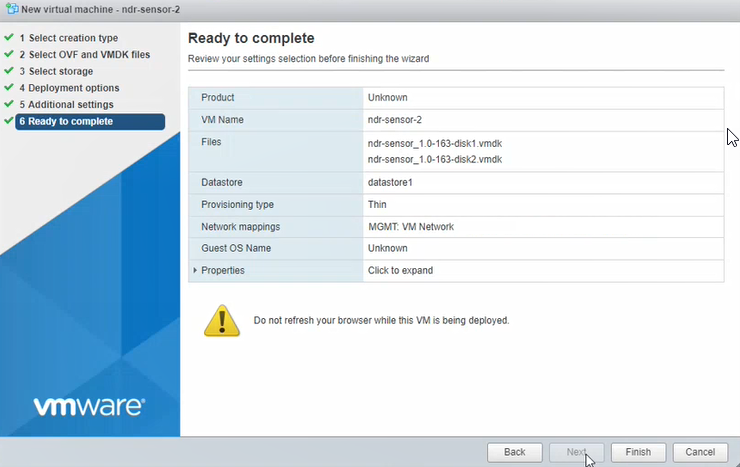
Click Finish. Wait for the new VM to appear in the VMs list. This can take a few minutes.
-
Start the VM and wait for installation to complete.
The VM starts for the first time and checks that it can connect to the correct port groups and to the internet. Then it restarts. This can take up to 10 minutes.
-
In Sophos Fusion, go to My Products > NDR > Investigation Console. The green checkmark icon
 shows next to the investigation console.
The ZIP file you downloaded in Sophos Fusion contains the virtual drives, seed.iso file, and PowerShell script you need to deploy your VM.
To deploy the VM, do as follows:
- Extract the ZIP file to a folder on your hard drive.
- Go to the folder, right-click the
ndr-sensor.ps1file, and select Run with PowerShell. -
If you see a Security Warning message, click Open to allow the file to run.
You're prompted to answer a series of questions.
-
Give the VM a name.
- The script shows the folder where the VM files will be stored. This is a new folder in your default installation location for virtual drives. Enter
Cto allow the script to create it. - Enter the number of processors (CPUs) to use for the VM.
- Enter the amount of memory to use in gigabytes (GB).
-
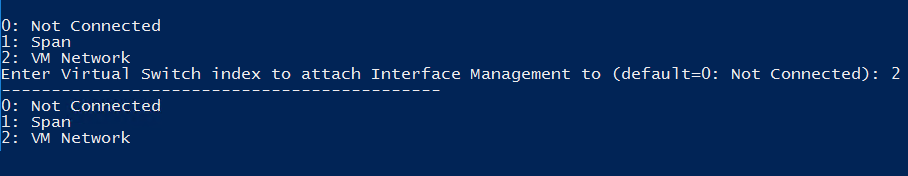
The script shows a numbered list of all your current vSwitches.
Select the vSwitch you want to attach the management interface to and enter its number. You set up this interface earlier in Sophos Fusion in Internet-facing network port settings.
If you selected DHCP during setup, make sure the VM can get an IP address via DHCP.
-
You don't need to specify vSwitches for capturing network traffic. These settings are only relevant if you have Sophos NDR. Select any vSwitch as a placeholder and disconnect it in the VM settings later.
The PowerShell script sets up the VM in Hyper-V. You'll see an Installation Completed Successfully message.
-
Press any key to exit.
-
Open the Hyper-V Manager to see the VM added to the list of virtual machines. You can edit your settings if needed. Then start the VM.
The VM starts for the first time and checks that it can connect to the correct vSwitches and the internet. Then it restarts. This can take up to 10 minutes.
-
In Sophos Fusion, go to NDR > Investigation Console. A green checkmark icon
shows next to the investigation console name.
Add an NDR appliance
Now you add an NDR appliance to the investigation console.
You can't add an NDR appliance until your investigation console has registered with Sophos Fusion and shows a green checkmark icon .
-
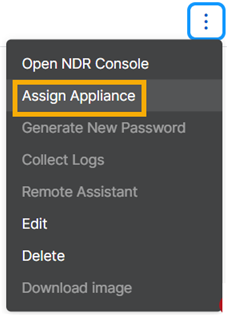
On the Investigation Console page, click the three dots on the right of the investigation console's row and select Add/Remove Appliances.
-
Select the appliance you want to add to the investigation console. To remove an appliance from the investigation console, deselect it.
An NDR appliance can only be assigned to one investigation console.
-
Click Save.
View investigation consoles
The table on the Investigation Console page lists investigation consoles you've already created with one of the following status icons:
- Green checkmark icon : The investigation console is connected and healthy.
- Yellow warning icon
 : The investigation console is connected, but there is an issue such as low disk space or high CPU.
- Red warning icon : The investigation console isn't connected to Sophos Fusion, including an investigation console that hasn't been deployed yet.
Sophos Fusion updates the status every five minutes.
The table shows the following information about each investigation console:
- Console Name: The name of the investigation console. Click the name to open the investigation console. See Open an investigation console.
- Appliances: The number of NDR appliances assigned to the investigation console.
- Type: The virtual platform the investigation console is on, such as VMware or Hyper-V.
- Version: Investigation console version.
- CPU, Memory, System Storage, and Data Storage: Usage percentages.
- IP Address: The IP address of the investigation console's management interface.
- Log requested: The date of the most recent request for troubleshooting logs. See Collect logs.
You can take the following actions:
- Click the Filter icon to filter the list by type.
- Click the Refresh icon above the table to reload the list and update the usage metrics.
- Click the three dots on the right of a row to see actions available for the investigation console.
Note
You can only download the image after you create the investigation console and before you deploy and register it.
View assigned appliances
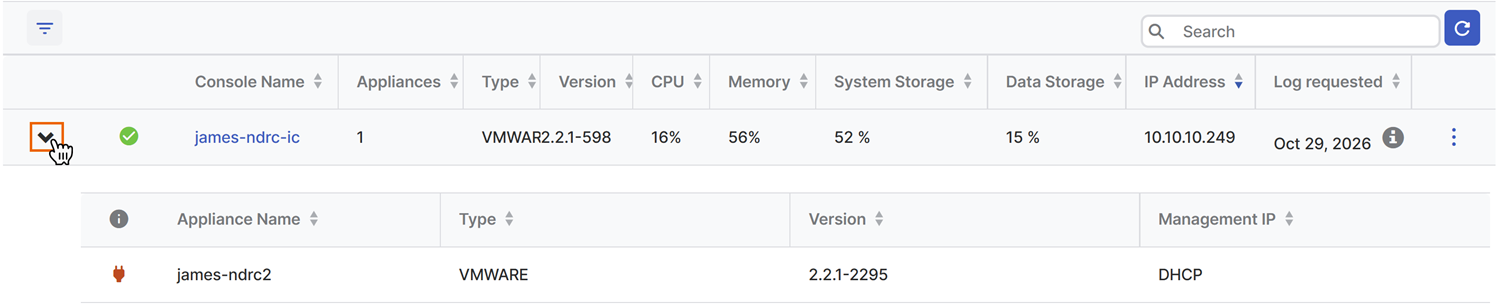
On the Investigation Console page, click the arrow next to an investigation console name to see the following details of the NDR appliances assigned to it:
Note
These details are for the assigned NDR appliances, not the investigation console. The investigation console only has a management interface.
- Appliance name: Name of the NDR appliance.
- Type: Virtual platform hosting the appliance.
- Version: Version of the virtual platform.
-
Management IP: The IP address of the appliance's management interface if it's statically assigned, or DHCP if it's dynamically assigned.
The appliance uses this interface to communicate with Sophos Fusion and the investigation console.
Open an investigation console
When you open an investigation console, you leave Sophos Fusion and open the web interface on the investigation console VM. Your browser must be able to reach the investigation console's IP address.
To open an investigation console, do as follows:
- Go to My Products > NDR > Investigation Console.
- Find your investigation console in the list.
-
Click the three dots on the right of the row and select Open NDR Console.
You see a warning that you're leaving Sophos Fusion.
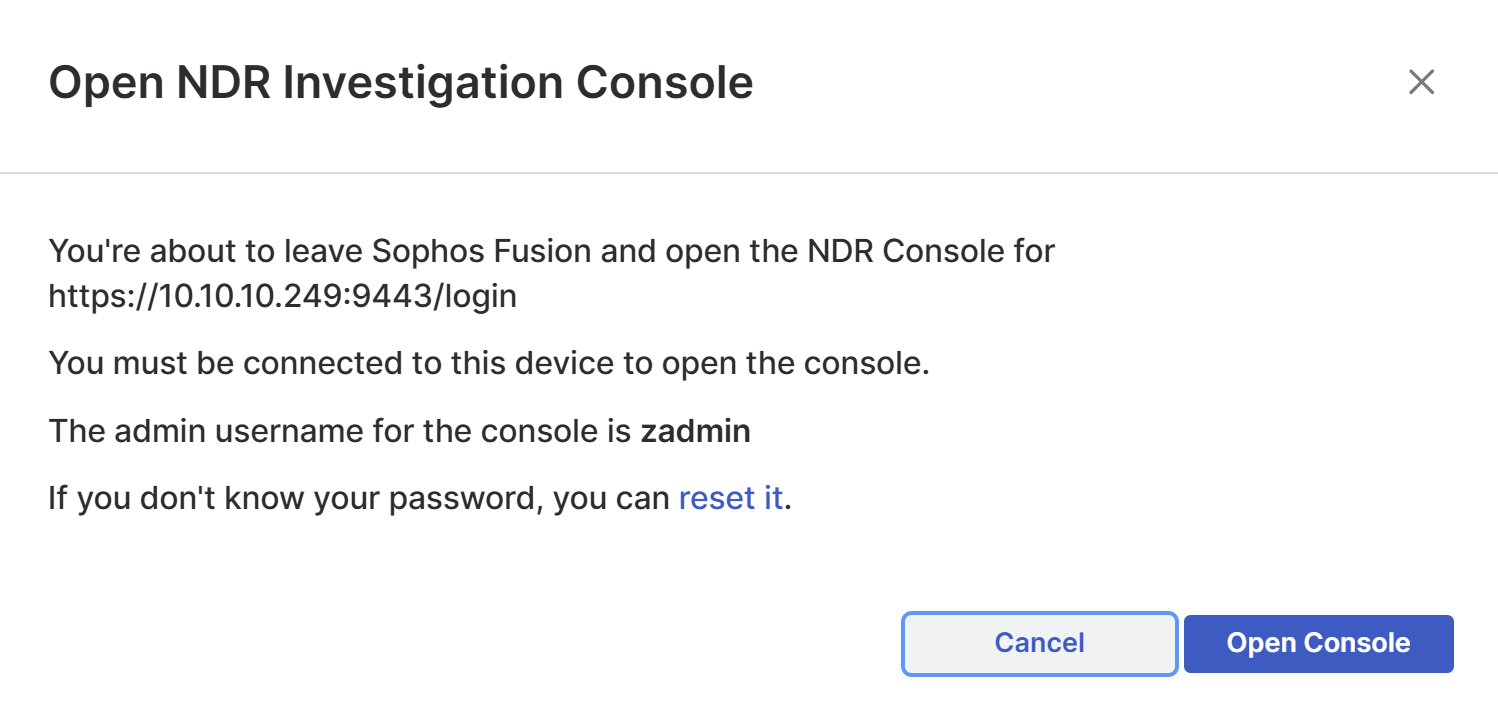
If you've forgotten your password, click reset it.
-
Click Open Console.
Reset an investigation console password
You can reset the password you use to access an investigation console.
- Go to My Products > NDR > Investigation Console.
- Click the three dots on the right of the investigation console row and select Generate New Password.
-
Click Reset.
Copy the password and store it safely. It's only shown once. You can't retrieve it later.
Collect logs
To collect troubleshooting logs from an investigation console for Sophos Support, do as follows:
- Go to My Products > NDR > Investigation Console.
-
Click the three dots on the right of the investigation console row and select Collect Logs.
The Log requested column shows the request date with an Info icon .
-
Click the Info icon to see the request details and the URL for the uploaded log file.
- Copy the URL and paste it into your support case.
Remote Assistant
Sophos Support can remotely connect to an investigation console for troubleshooting. You can give them access for up to seven days as follows:
Note
The investigation console must be online to use remote assistant.
- Go to My Products > NDR > Investigation Console.
- Click the three dots on the right of the investigation console row and select Remote Assistant.
-
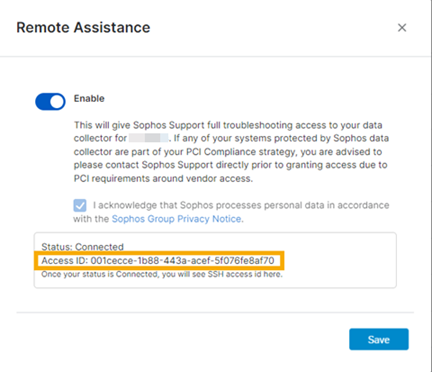
In the Remote Assistance dialog, do as follows:
- Select Enable.
- Select the checkbox to acknowledge the Sophos Group Privacy Notice.
- Click Save.
Sophos Fusion requests an Access ID from the appliance. When it's available, it's shown in the dialog.
-
Copy the Access ID and send it to Sophos Support. They use it to access your investigation console.
Remote assistance turns off automatically after seven days. To turn it off manually, go back to the Remote Assistance dialog, clear Enable, then click Save.
Edit investigation console settings
You can edit an investigation console's name, description, Network Port, and Internet-facing network port settings as follows:
- Go to My Products > NDR > Investigation Console.
- Click the three dots on the right of the investigation console row and select Edit.
-
Edit the investigation console settings.
You can't edit the virtual platform or hostname.
-
Click Save.
You don't need to update the investigation console VM manually. Sophos Fusion sends the configuration changes to it automatically.
Delete an investigation console
To delete an investigation console, do as follows:
- Go to My Products > NDR > Investigation Console.
-
Click the three dots on the right of the investigation console row and select Delete.
Note
The confirmation dialog lists any appliances that will be removed from the investigation console.
Deleting the investigation console doesn't delete its virtual machine. Shut down and delete the VM in VMware or Hyper-V.
You can assign appliances from the deleted investigation console to another investigation console.