Identity response actions
You can configure response actions for identity accounts in Microsoft Entra ID and on-premises Active Directory (AD) environments using actions, connectors, and playbooks. For guidance, see these resources:
If you've already configured Microsoft Entra ID connectors and playbooks in Sophos Fusion, you don't need to do this step again.
Entra ID response actions
If your identity integration uses Microsoft Entra ID, you can use the Microsoft Graph API connector to configure actions and playbooks. For example, you can disable or enable a user account, or reset a password.
Hybrid environments
If Microsoft Entra Connect Sync synchronizes on-premises AD accounts to Entra ID, disabling a user in Entra ID can be reversed by the next synchronization. For details, see Hybrid Entra ID behavior for response actions.
To set up Entra ID response actions, do as follows:
- Add a connection using the Microsoft Graph API connector. See Configure a connection.
- Use the connection in actions, such as Disable User or Enable User, or in playbook templates, such as Microsoft Entra ID Disable User or Microsoft Entra ID Force Password Reset. See Configuring actions and Playbook templates.
On-premises response actions
If your Active Directory environment uses Lightweight Directory Access Protocol (LDAP), you can configure response actions for on-premises accounts. This lets playbooks and actions connect directly to your AD or LDAP directory services without exposing them to the internet.
To do this, deploy an on-premises data collector and add the On-Premise Automation Connector application to the collector.
Note
The system that hosts the On-Premise Automation Connector application must have network access to your AD or LDAP directory services. The connector supports LDAP authentication for connecting to these services.
To set up on-premises response actions, do as follows:
- Deploy an on-premises data collector if you haven't already. See On-premises data collector.
- Add the On-Premise Automation Connector application to the data collector and configure it for LDAP authentication so it can reach your AD or LDAP directory services. See Add an On-Premise Automation Connector to a data collector.
- Add a connection using the On-Premise Automation Connector. See Configure a connection for on-premises use.
- Use the connection in actions or playbooks to run response actions, such as disabling an AD account.
Automated response actions
After adding connections, you can configure automated response actions for identity findings using the User Automated Response Actions playbook template. For details on configuring templates, see Playbook templates.
Use the following guidance for the Playbook Execution configuration:
-
For the Trigger Type, choose these settings:
- Source: Identity Findings
-
Events: Created
Warning
Choosing Updated instead of Created causes the playbook to run whenever the finding is updated. Because posture checks generate update events, the playbook might run multiple times per day and repeatedly reset a user's password.
-
For When does this playbook run?, select Only When to enter a Common Expression Language (CEL) expression that determines when the playbook runs. See Get started with CEL.
Example
These settings run the response action whenever a new Credential Compromise finding with a critical or high severity is created:
- Trigger Type: Platform Events
- Source: Identity Findings
- Events: Created
- When does this playbook run?: Only When
-
CEL Expression:
inputs.identityFindings.new.severity>=0.6&&inputs.identityFindings.new.check.category=="credential_compromise"
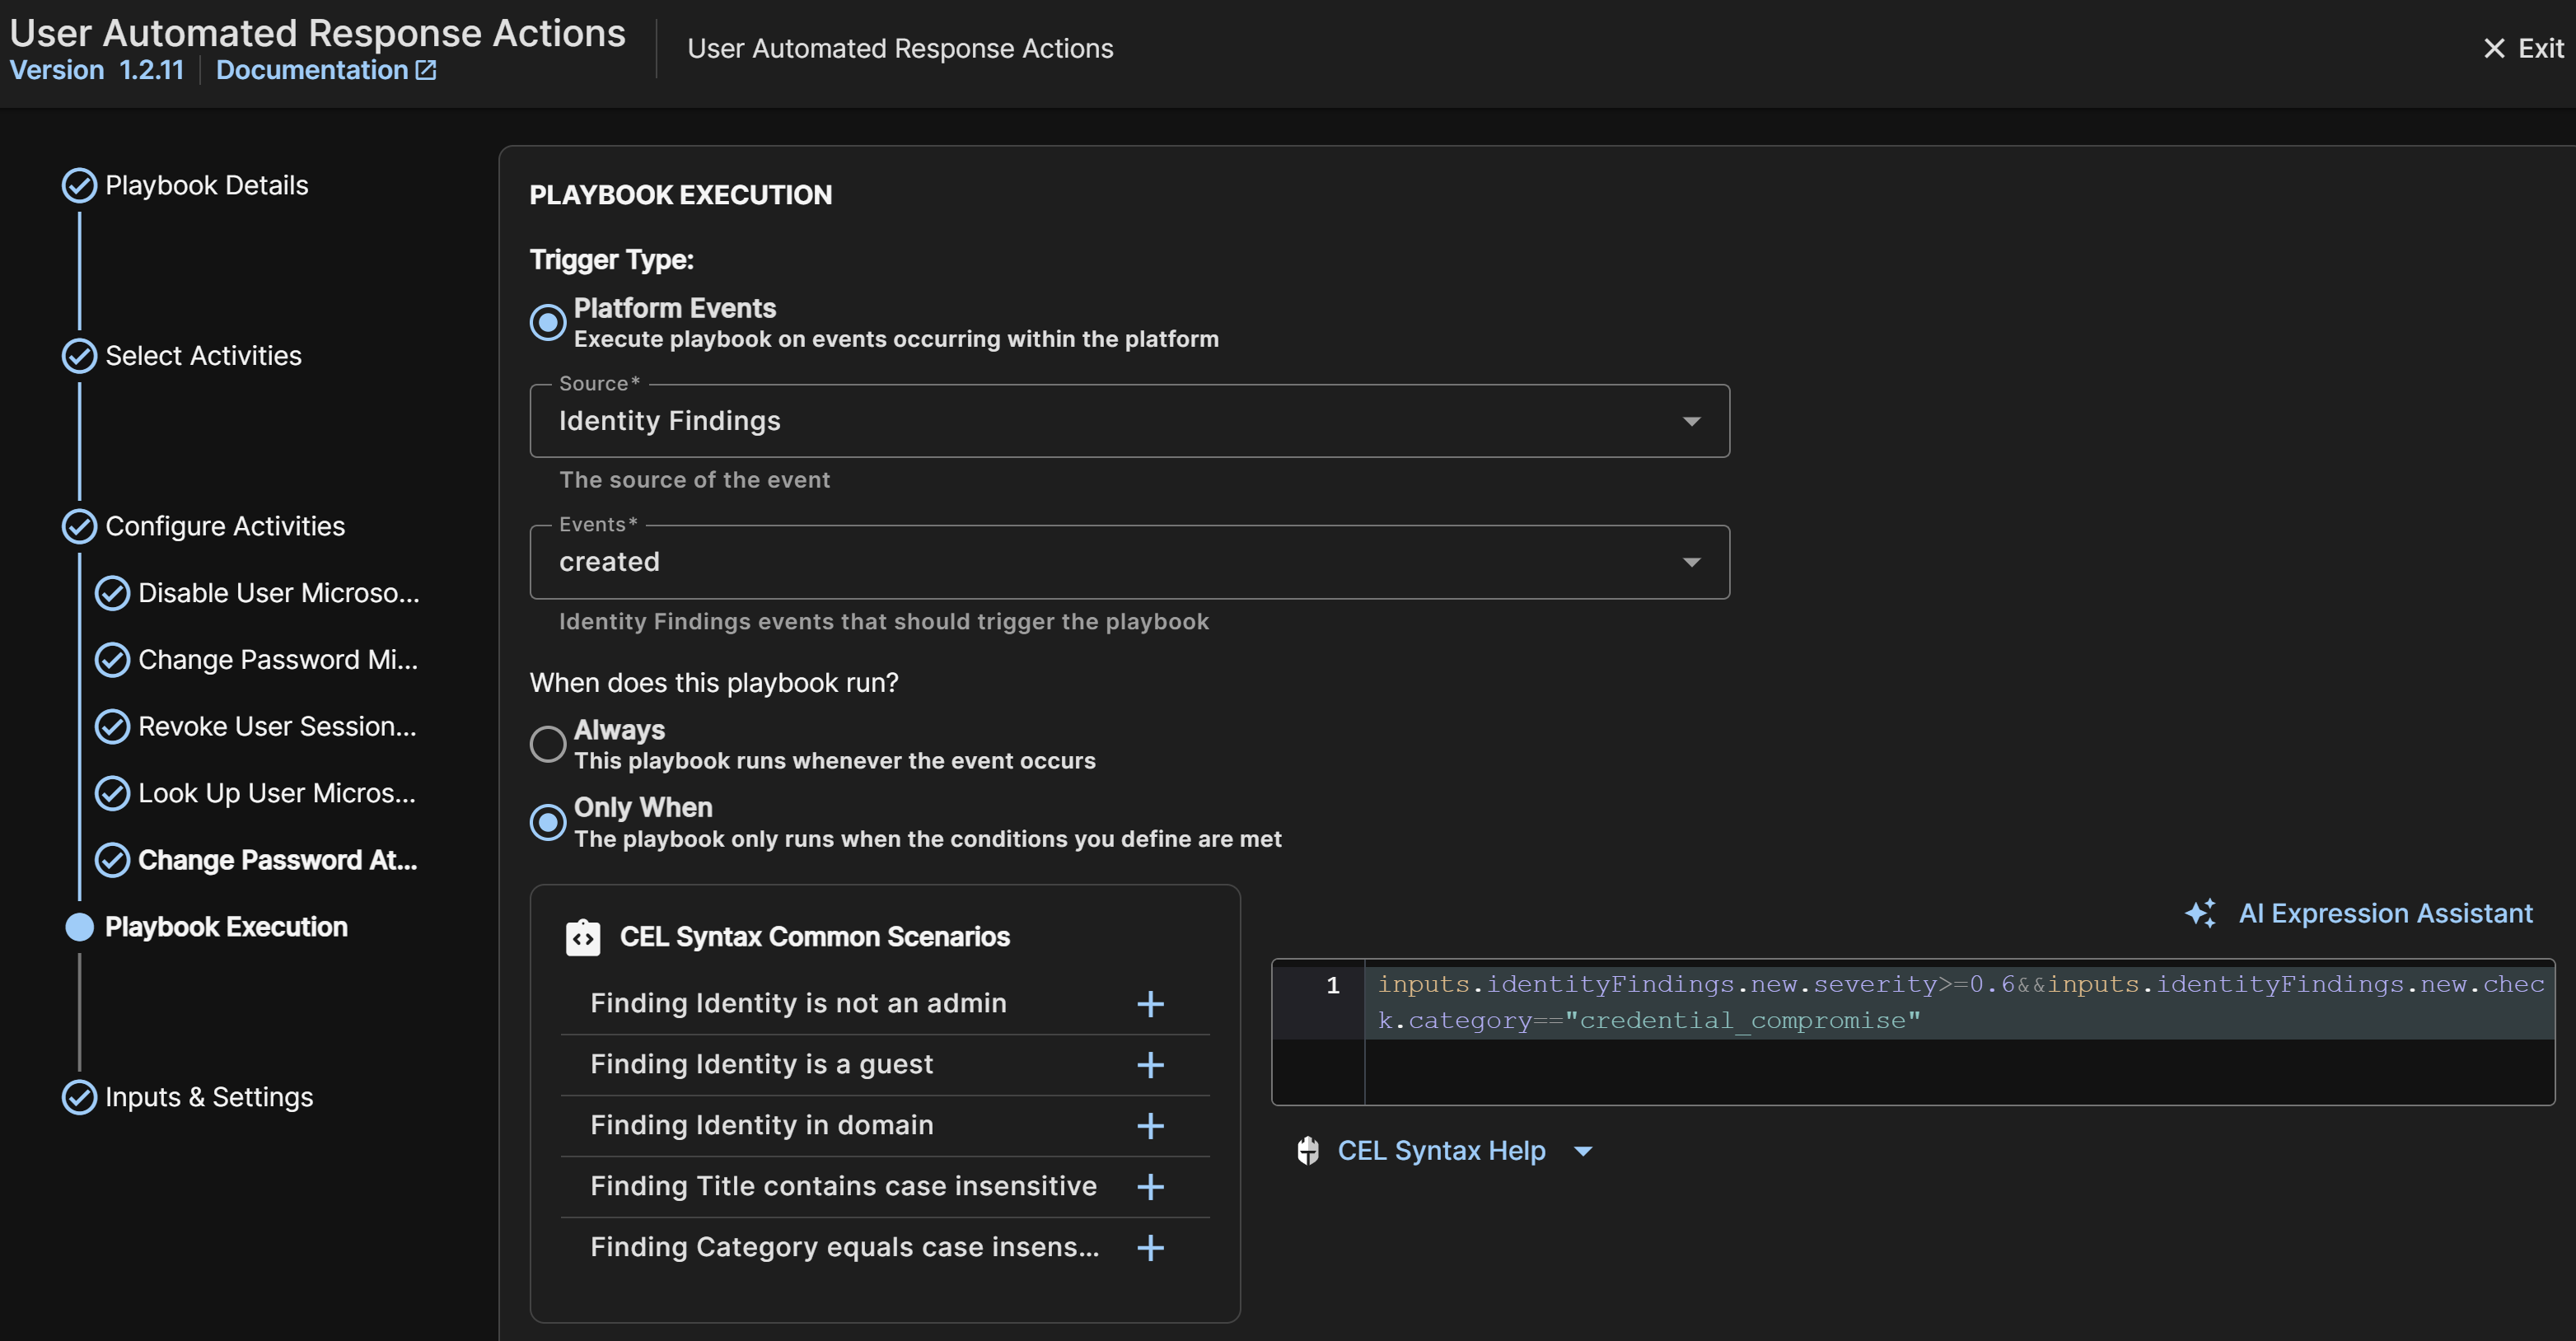
The examples below show additional matches you can perform with CEL expressions to customize what triggers the response action:
Finding with critical or high severity and a specific title
inputs.identityFindings.new.severity >= 0.6 && inputs.identityFindings.new.check.title.startsWith('Application shall not have unclaimed DNS')
Finding with critical or high severity for an application
inputs.identityFindings.new.severity >= 0.6 && inputs.identityFindings.new.primaryReference.derivedType == "APP"
After you save and enable the playbook, the configured response action runs automatically when findings match the trigger criteria.
Hybrid Entra ID behavior for response actions
In hybrid environments, disable users in on-premises AD or by using an on-premises LDAP response action.
On-premises AD can override cloud response actions.
In a hybrid Entra ID environment, Microsoft Entra Connect Sync treats the on-premises AD account as the authoritative source. If you disable a user in Entra ID but leave the account enabled in on-premises AD, the next synchronization can re-enable the account.
This is normal Microsoft sync behavior and can't be controlled from the cloud side alone.
For more information, see What is Microsoft Entra Connect?.