Classic Sophos NDR on ESXi
Classic Sophos NDR is being replaced by Sophos NDR.
For migration options, see Migrate to Sophos NDR.
Currently, classic Sophos NDR supports VMware ESXi 6.7 or later.
The main steps are as follows:
- Check the requirements below.
- Configure an integration. This configures an image to use on a VM.
- Configure your switches so NDR can see traffic.
- Download and deploy the image on your VM. This becomes the appliance.
Requirements
-
Currently, Sophos supports VMware ESXi 6.7 Update 3 or later. To check your version, see the following articles:
-
The VM that runs the appliance must meet general system, processor, and network access requirements. See Minimum system requirements and CPU requirements.
- For a quick guide on resizing the VM for optimal performance, see Classic Sophos NDR VM appliance size guide.
Note
We support VMware Enhanced vMotion Compatibility (EVC) clusters, provided you've selected the following:
- Skylake generation or later CPU
- VMware hardware version 11 or later
Note
We don't support VMware Cloud deployments.
Configure an integration
To configure the integration, do as follows:
- Sign in to Sophos Fusion as an Admin or Super Admin.
- Go to Security Operations > Integrations > Marketplace.
- Click Sophos NDR.
- Click Continue to be redirected to the classic Threat Analysis Center, where you configure the integration.
-
On the NDR page, in Data Ingest (Security Alerts), click Add Configuration.
Integration setup steps appears.
Configure the VM
-
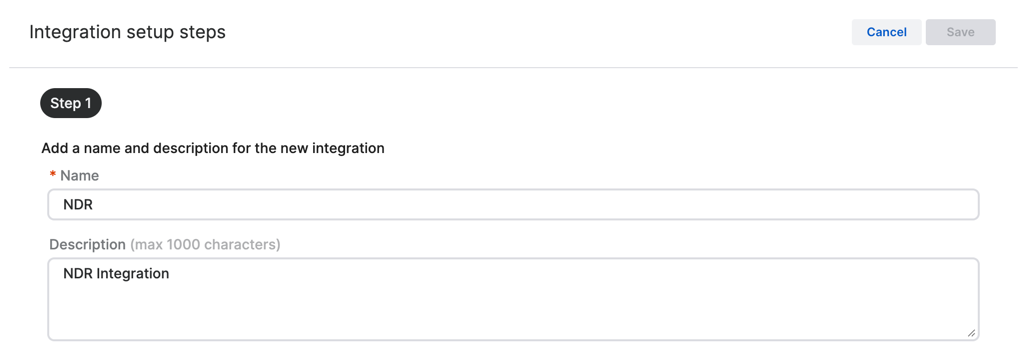
In Step 1, enter a name and description for the integration.
-
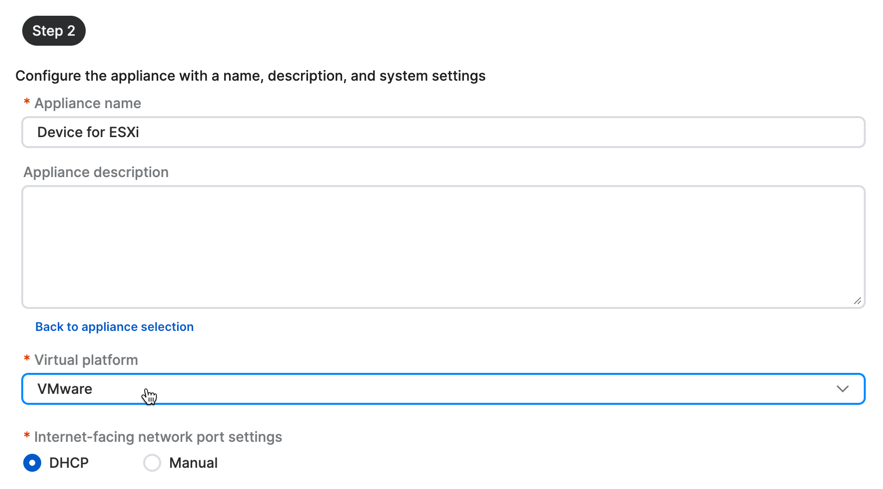
In Step 2, select or create the appliance that will collect NDR logs.
You can only have one NDR integration per appliance.
If you need a new appliance, click Create new appliance and follow the instructions in the next step.
If you want to use an existing appliance, select it from the drop-down list and skip to Step 3 to set exclusions.
-
To create a new appliance, do as follows:
- Enter the appliance name and description. You must enter a unique name.
- Select the virtual platform (VMWare).
-
Specify the internet-facing network ports.
-
Select DHCP to assign the IP address automatically.
Note
If you select DHCP, you must reserve the IP address.
-
Select Manual to specify network settings.
Example
- IP address: 10.0.252.5
- Subnet mask: 255.255.255.0
- Gateway address: 10.0.252.1
- DNS 1: 8.8.8.8
- DNS 2: 8.8.4.4
-
-
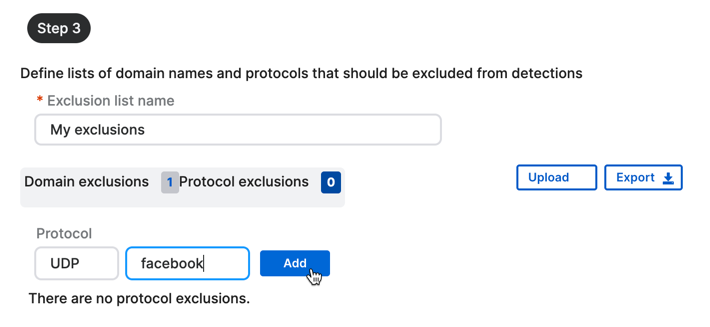
In Step 3, exclude specific domains and protocols from checking. For example, you might do this if you have a domain that causes false positives.
You can set up your exclusions later, but you must enter an exclusion list name now.
- Enter an Exclusion list name.
- To exclude a domain, click Domain exclusions. Enter the domain name, for example,
sophos.com, and click Add. -
To exclude a protocol, click Protocol exclusions. You can enter information in either or both of the fields:
- In the first field, enter a master protocol. For example,
TCPorUDP. - In the second field, enter a sub-protocol (website). For example,
facebook.
If you enter information in both fields, we assemble them into one string with a single dot separator.
We don't recommend excluding a master protocol completely. Only do this if a high-traffic protocol that isn't usually risky, like a routing protocol, generates too much data.
- In the first field, enter a master protocol. For example,
-
Click Add.
You can export your exclusions as a JSON file. You can also upload exclusions to the list from a previously exported JSON file.
-
Click Save.
In the NDR page, you see the new integration in the list of configured integrations.
Next, configure your switches so the NDR appliance can monitor your network traffic.
Configure your switches
Before you download and deploy the Sophos NDR VM, you must set up port mirroring, also known as Switched Port Analyzer (SPAN). This forwards a copy of incoming and outgoing traffic from a switch's ports or VLANs to another switch port for analysis.
You must configure port mirroring for both virtual internal and physical external network traffic.
When you deploy your NDR VM appliance later, you’ll be able to connect it to your SPAN ports so that NDR can monitor network traffic.
Port mirroring involves the following steps:
- Configure virtual switches.
- Configure a physical switch.
Configure virtual switches
To set up port mirroring for virtual, internal switches, do as follows:
-
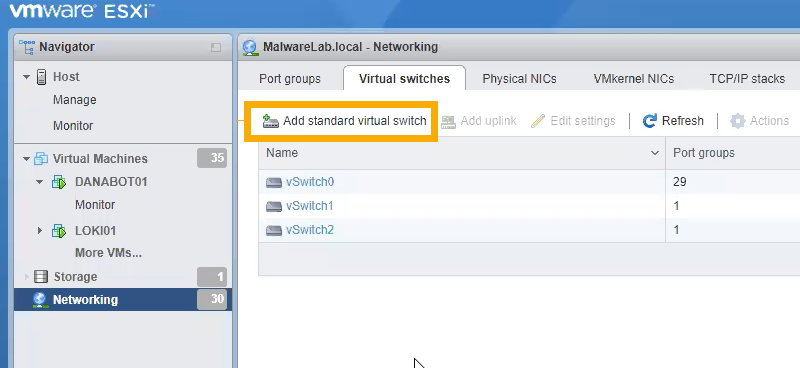
In ESXi, go to Networking. On the Virtual switches tab, select a switch to use for port mirroring.
If you don’t already have a switch to use, click Add standard virtual switch to add a new one and add port groups to it.
-
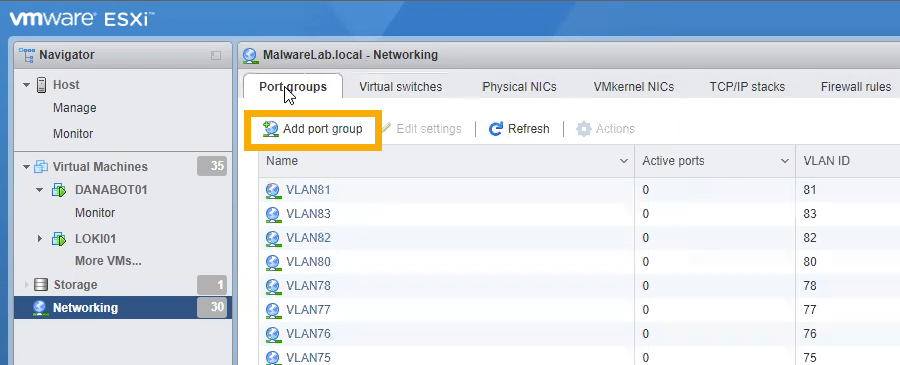
On the Port groups tab, click Add port group.
-
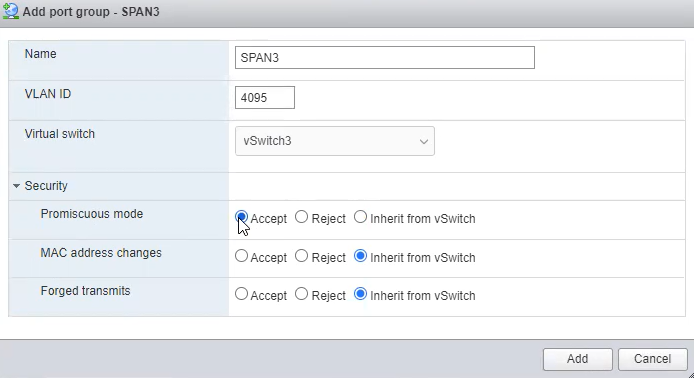
In the settings for the new port group, do as follows:
- Enter a name.
- Set the VLAN ID to 4095. This allows all other port groups already on the switch to forward traffic to the new port group.
- Click Security and set Promiscuous mode to Accept.
- Click Add.
You've set up forwarding for traffic on your virtual internal network. Next, do the same for physical external traffic, as described in the steps that follow.
-
In ESXi, select or create another virtual switch to handle external traffic from a physical switch on your network.
-
Configure the switch as follows:
- Go to Port groups and click Add port group.
- Enter a name.
- Set VLAN ID to 4095.
- Click Security and set Promiscuous mode to Accept.
Next, you connect your virtual switch to your physical network so that it can receive external traffic.
-
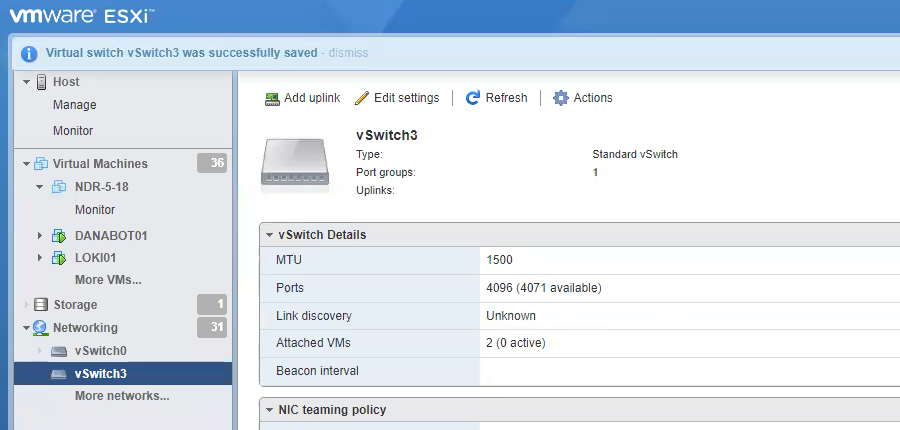
In the ESXi left menu, go to Networking and select the switch you want to use for external traffic.
-
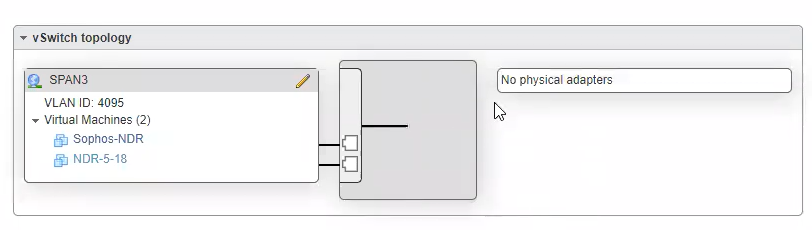
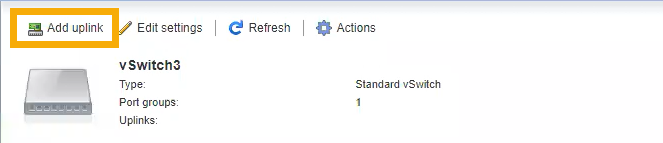
In the switch details, look for vSwitch topology. You can see “No physical adapters”.
-
Click Add uplink.
-
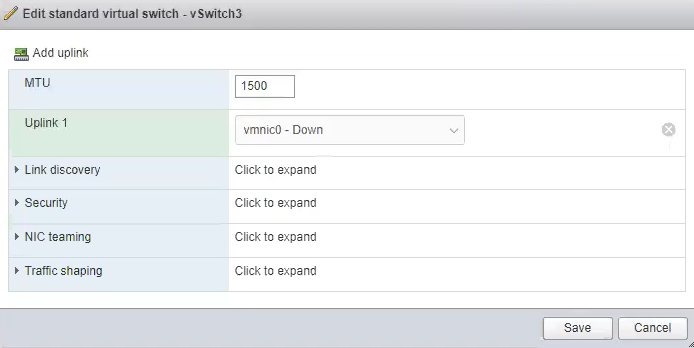
In Uplink 1, select an available NIC (Network Interface Card). This connects the virtual switch to a port on your ESXi server.
-
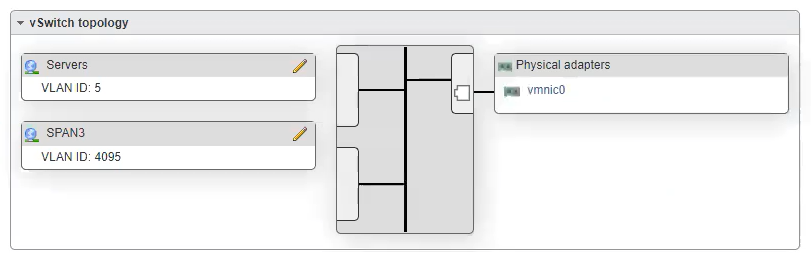
In Network topology, check that you can see a physical adapter connected.
-
Go to your physical switch and use a cable to connect directly to the port on your ESXi server.
Next you need to set up mirroring on your physical switch.
Configure a physical switch
This section describes how to set up port mirroring on a Sophos switch. The setup steps for other switches differ.
To set up mirroring, do as follows:
- In Sophos Fusion, go to My Environment > Switches.
-
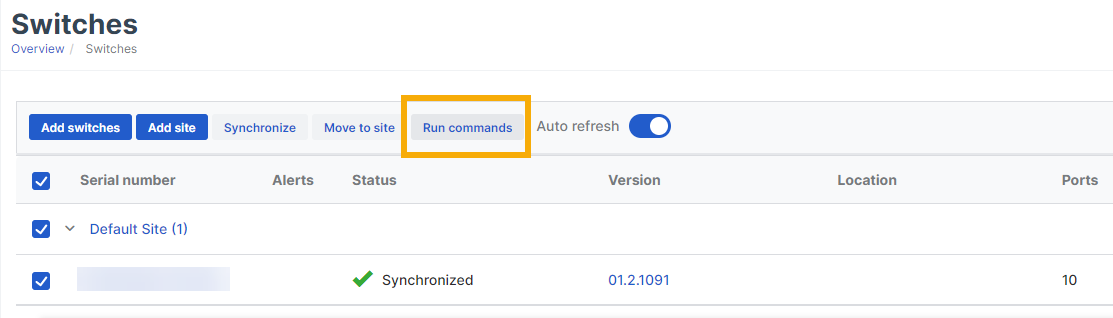
Select the switch you want to configure and click Run commands.
-
In the Run switch commands console, enter the commands to mirror all traffic. In this example, the commands will mirror all incoming and outgoing traffic on ports 1-4, and send it out on port 8.
configure terminal
monitor session 1 destination interface gigabitethernet 0/8 allow-ingress
monitor session 1 source interface gigabitethernet 0/1 both
monitor session 1 source interface gigabitethernet 0/2 both
monitor session 1 source interface gigabitethernet 0/3 both
monitor session 1 source interface gigabitethernet 0/4 both
save
end
show monitor session 1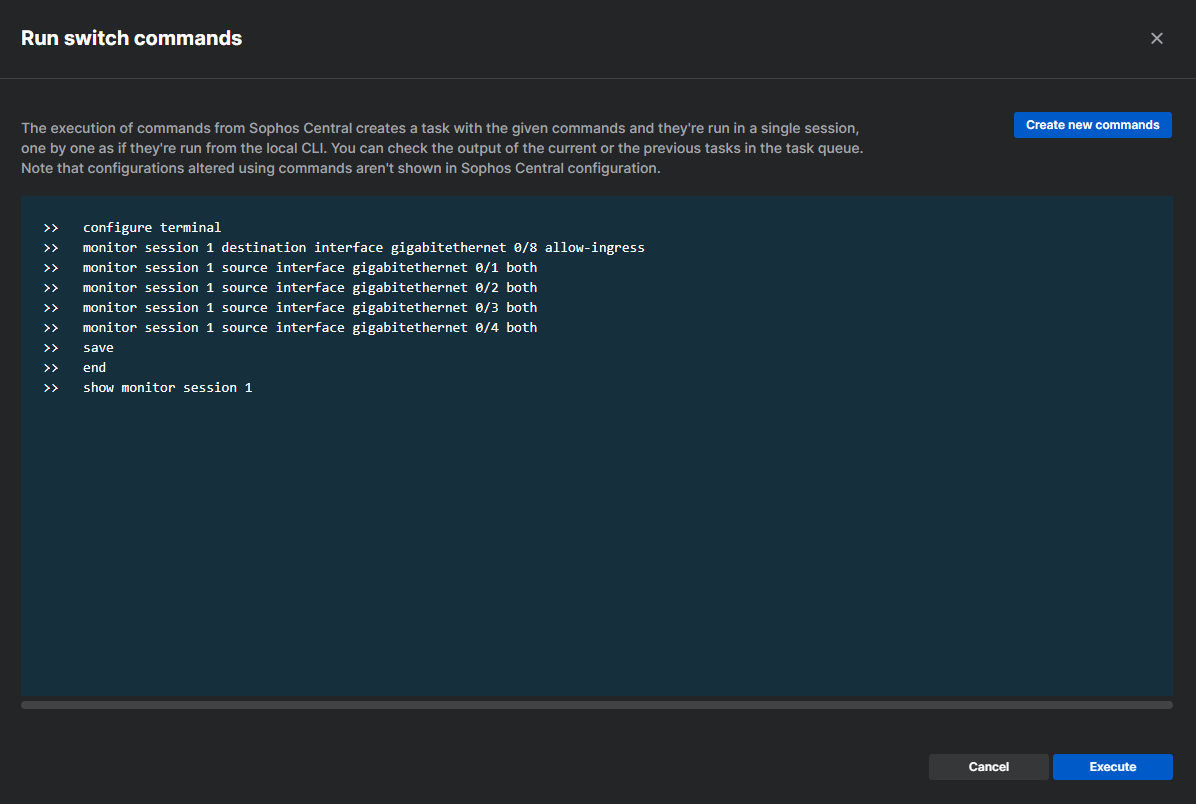
-
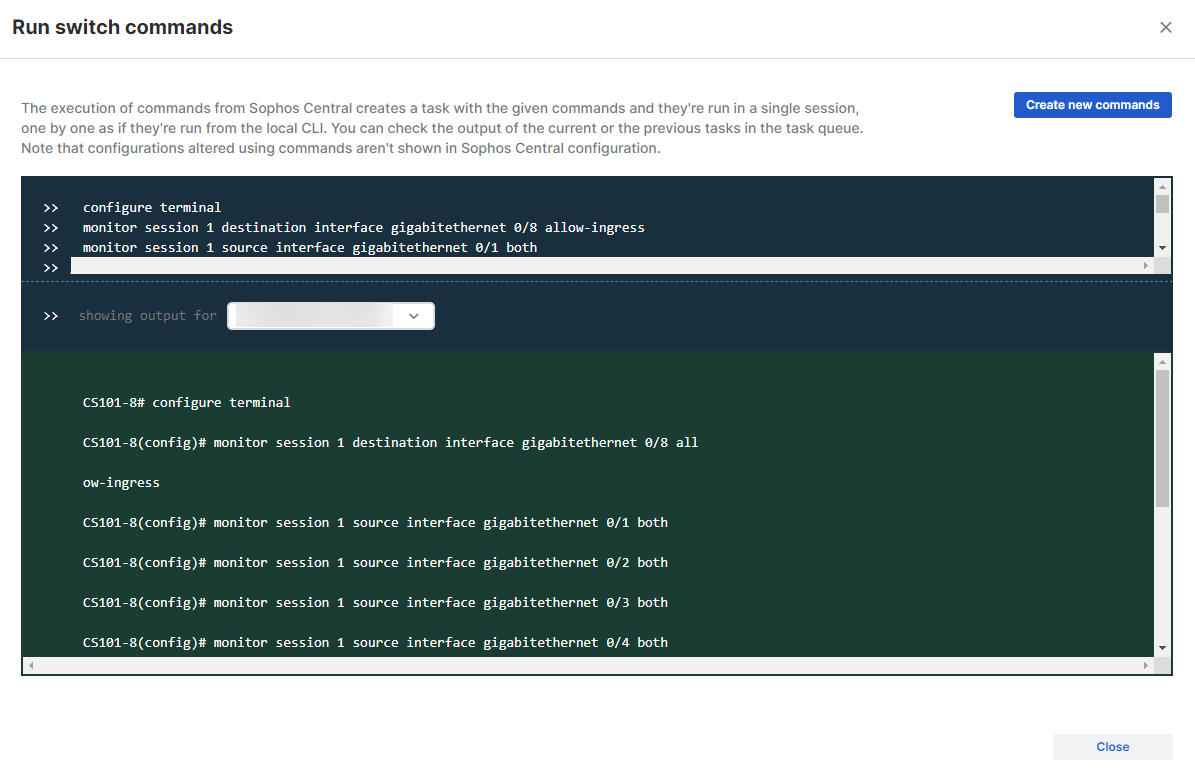
Click Execute. The console shows the commands as they run on a green background.
-
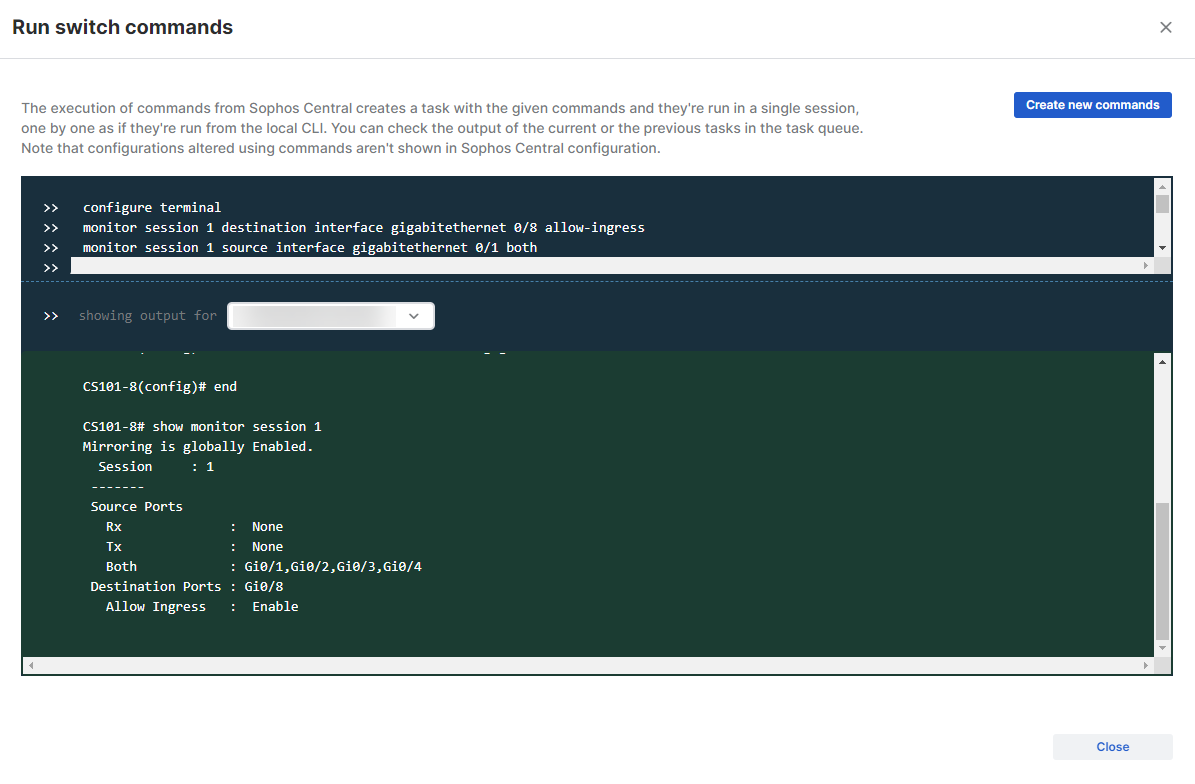
When the last command is run, the console shows the completed configuration. Click Close.
You've finished setting up traffic forwarding to SPAN ports. Later, you'll configure Sophos NDR to monitor that traffic.
Download the VM image
Now you download the NDR image you need to deploy and boot the new VM.
-
Next to the new integration, click the three dots in the Actions column, and click Download image.
You see the download start.
-
Hover over the icon to the left of the integration name. You now see "Waiting for deployment".
You're ready to deploy the VM.
Deploy the VM
Restriction
If you're using ESXi, the OVA file is verified with Sophos Fusion, so it can only be used once. If you have to deploy a new VM, you must create the OVA file again in Sophos Fusion.
Warning
If you're deploying the OVA on an ESXi host running in an Enhanced vMotion Compatibility (EVC) cluster, EVC must be in Skylake or later mode.
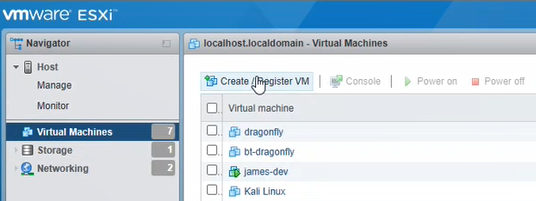
- Go into your ESXi host.
-
Select Virtual Machines and click Create/Register VM.
-
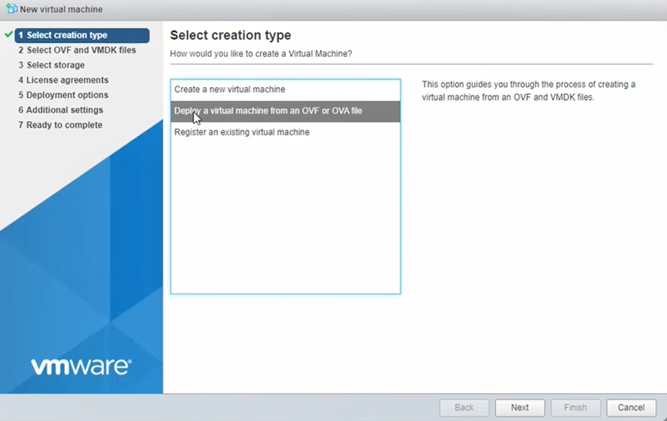
In Select creation type, select Deploy a virtual machine from an OVF or OVA file. Click Next.
-
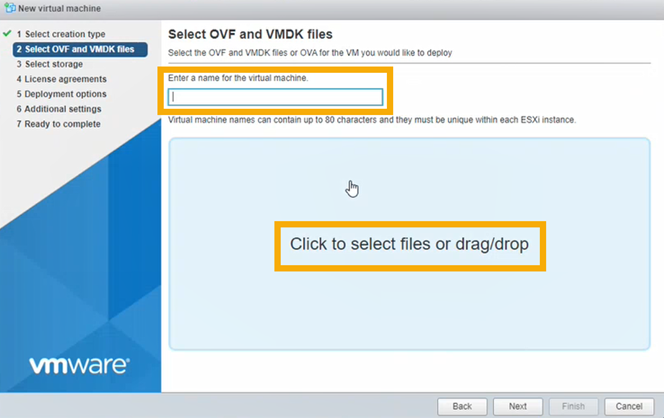
In Select OVF and VMDK files, enter a VM name.
Click the page to select files. Select the OVA file ndr-sensor.ova. Click Next.
-
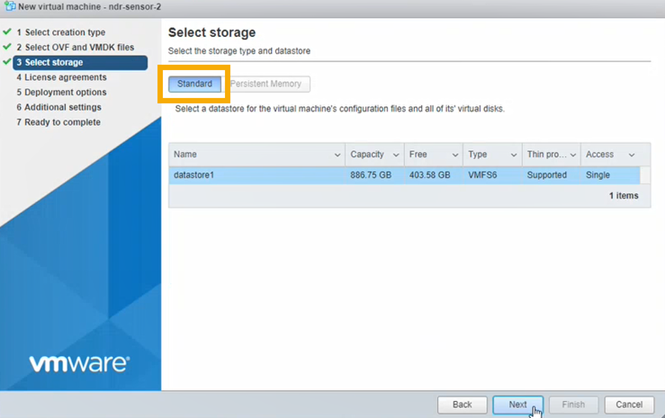
In Select storage, select Standard storage. Then select the datastore where you want to put your VM. Click Next.
-
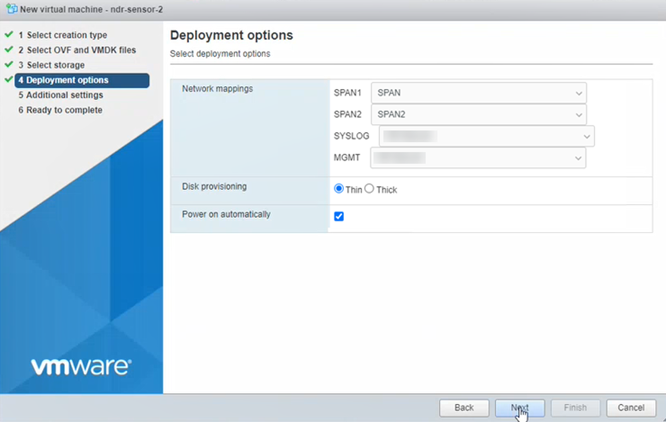
In Deployment options, enter settings as follows.
- In SPAN1, select the port group that will receive SPAN traffic for the NDR application. You configured this earlier. See Configure your switches.
-
In SPAN2, select a second port group that will receive SPAN traffic and needs monitoring (if you have one). For example, you might have a physical switch and a vSwitch that doesn't send traffic to the physical switch.
If you use SPAN2, you must increase the number of CPUs for the VM to at least 8. See Classic Sophos NDR VM appliance size guide.
-
SYSLOG isn't needed for the Sophos NDR integration. Select any port group as a placeholder and disconnect it in the VM settings later.
-
In MGMT, select the management interface. This interface lets the appliance send data to Sophos Fusion.
You set up this interface earlier in Sophos Fusion in Internet-facing network port settings.
If you selected DHCP during appliance setup, make sure the VM can get an IP address via DHCP.
-
In Disk Provisioning, make sure Thin is selected.
- Make sure Power on automatically is selected.
- Click Next.
-
Skip the Additional settings step.
-
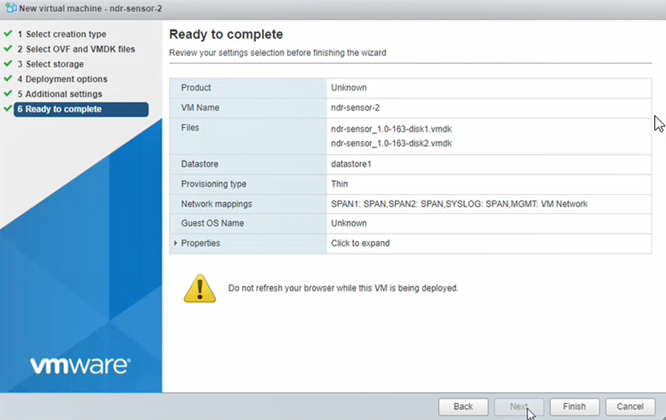
Click Finish. Wait for the new VM to appear in the VMs list. This can take a few minutes.
-
Power on the VM and wait for the installation process to complete.
The VM boots for the first time and checks that it can connect to the correct vSwitches and to the internet. Then it reboots. This can take up to 10 minutes.
Warning
Don't interrupt this process.
-
In Sophos Fusion, go to the NDR Integrations page and refresh it. The VM's status is now Connected.
If the VM status is Connected but it doesn't appear to be working, check the Dragonfly service status in the Appliance Manager dashboard's Advanced tab. See Troubleshooting.
If you see in the console that the Dragonfly service is Pending, and your VM is in an Enhanced vMotion Compatibility (EVC) cluster, verify that the EVC mode is Skylake or later.
The Sophos NDR VA doesn't support running in EVC clusters in Sandy Bridge mode.