Detection severity and confidence
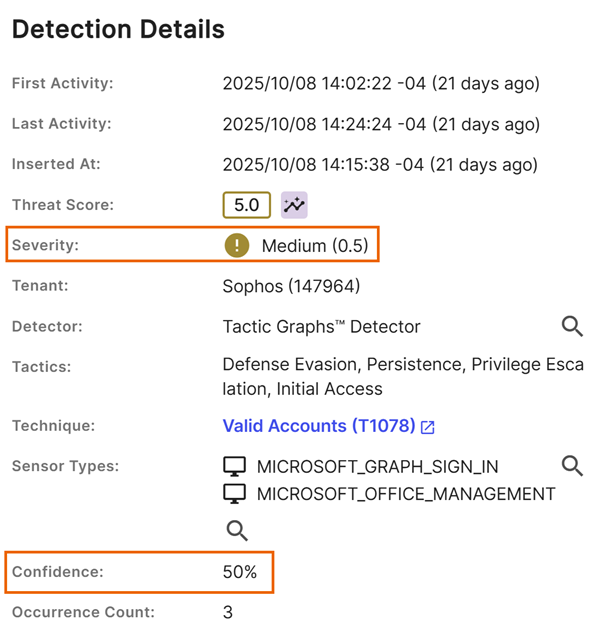
Severity and confidence scores make it easier for you to prioritize detection triage in your environment and address the most important detections first. You can see the severity and confidence of a detection in the detection details. For more information, see Detection details.
Tip
Threat Score is a context-aware priority value assigned to detections by the patent-pending Prioritization Engine. For more information, see Threat Score.
Severity
Severity is a measure of the potential threat an activity poses. The severity score ranges from 0.01 to 1. The greater the score, the greater the potential threat posed by the activity. Severities have the following ratings:
- Informational: 0 to 0.199
- Low: 0.2 to 0.399
- Medium: 0.4 to 0.599
- High: 0.6 to 0.799
- Critical: 0.8 to 1
Note
If the detection's severity level has changed, a message shows in the detection details.
Confidence
Confidence is a measure of how confident we are that the detection is accurate and represents malicious activity. The confidence score ranges from 1 to 100. The greater the score, the more confident we are that the detection indicates genuine malicious activity.
Determining severity and confidence
Each detector collects different data from your environment to monitor for malicious activity and uses different aspects of this data to determine a severity and confidence score. For more information on available detectors, see Detectors.
For example, the Domain Generation Algorithm (DGA) Detector is a machine-learning-based detector that computes the probability that a domain is potentially an indicator of malicious activity. Both severity and confidence scores are based on the probability computed by the detector.
Other detectors define both severity and confidence statically, such as the Tactic Graphs™ Detector, which has a static severity and confidence score defined per adversary tactic. Similarly, the Taegis Watchlist Detector uses a static severity and confidence score set by the security researchers who created the watchlist.