Events
An event is an individual security-related occurrence, such as an ingested log, from a single point in time within your environment that has been normalized to use a standardized format for efficient access by software and humans. Events are visible in search results, cases, and from detection details. The details displayed for each event vary by event type and available data.
When viewing tables of events, click the event title to view some of its essential details in a slide-out. This allows you to continue browsing the results table without losing your place or filters. To view the full details of the event in a new tab, click the icon.
Tip
Adjust the width of the slide-out by holding and dragging it.
Event types
The following event types can be referenced throughout Security Operations:
| Event type | Search schema | Definition |
|---|---|---|
| Antivirus | antivirus | Events related to malware activity on hosts and networks. |
| API Call | apicall | Instances in which a process attempted (successfully or not) to call an operating system API. |
| Auth | auth | Activities including login successes & failures, logoffs, etc. |
| Cloud Audit | cloudaudit | Audit events from cloud-based applications and cloud-hosted infrastructure. |
| Detection Finding | detectionfinding | Detections generated by endpoint agents, or other sources external to Sophos Fusion. |
| DHCP | dhcp | Records of client and server DHCP activity, such as IP address assignments. |
| DNS | dnsquery | Records of domain name resolution requests by hosts. |
email | Events from email security services related to techniques such as phishing and spam. | |
| Encrypt | encrypt | Events related to SSL/TLS connection and X.509 certificate metadata. |
| File Modification | filemod | Instances in which a process attempted to create, modify, write, or delete a file. |
| Generic | generic | Stores all raw log messages from syslog and some other ingestion sources. Note: Generic events may also get normalized into other event types. |
| HTTP | http | Details on HTTP connections. For example, from proxy server logs. |
| Management | managementevent | Instances in which management information has been accessed from hosts in an enterprise environment, for example, via WMI for Windows. |
| Netflow | netflow | Network traffic information from in and out of the box communications, including source/destination IPs and ports. |
| NIDS | nids | Events from network intrusion detection and/or prevention systems. |
| Persistance | persistance | Events related to techniques such as Run keys, Scheduled Tasks, or Services, commonly used by attackers to maintain persistence in a compromised system. |
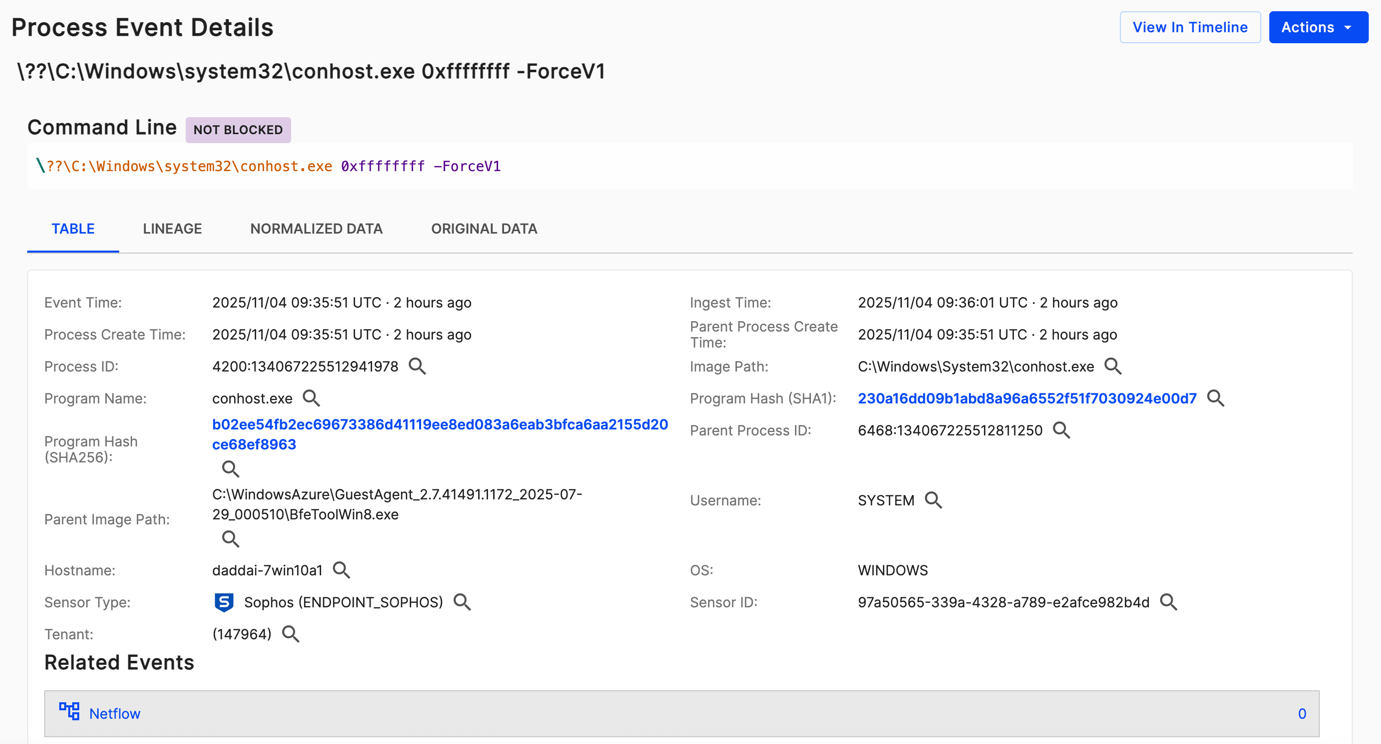
| Process | process | Arbitrary code execution in other live processes. Process events may have information about program launches and their associated command lines, parent/child relationships, and other information about programs and commands executed on the host, including target programs launched by main parent executables—for example, by PowerShell in Windows. |
| Process Module | processmodule | Events generated when libraries have been loaded by different processes. |
| Registry | registry | Properties of certain Windows registry entries, which may help to detect attacks. |
| Script Block | scriptblock | Executions of blocks of code (scripts) on a remote endpoint by an attacker or other entity. |
| Taegis Agent Detection | agentdetection | Detections reported by the Taegis Endpoint Agent. |
| Technique Finding | techniquefinding | Indicators of potentially malicious behavior observed by endpoint agents, or other sources external to Sophos Fusion. |
| Third Party Detection | thirdparty | The event record of detections produced on sources external to Sophos Fusion. |
| Thread Injection | threadinjection | Instances in which a thread has inserted and run code within the memory address space of a different target process. |
Event details
Most events include:
- Details table: A selection of normalized information about the event. The line items in the table vary depending on event type. For details, see Event types.
- Summary: A summary of what occurred in the event.
- Netflow diagram: Netflow and NIDS events may show a netflow diagram.
- File data: Links to relate filehashes if applicable.
- Normalized data: All normalized information about the event, in JSON format, in an expandable/foldable tree view.
- Original data: If available, the original, pre-normalization data for the event.
- View in Timeline: An option in some events to pivot from the selected event to a timeline view of related detections and events that occurred on the same host, by
host_id. For more information, see Timeline view.
Process event details
In addition to the above event details, process events include:
- Lineage: A visual, interactive view of the process tree. For more information, see Event Lineage and Process Tree.
- Related events: Direct links to advanced searches for netflow, thread injection, persistence, and script block events related to the current process event.