Integrate Cloudflare SSE
You can integrate Cloudflare SSE with Sophos XDR so that it sends data to Sophos for analysis.
Key steps
The key steps in a Cloudflare SSE integration are as follows:
-
Choose an ingest transport to send Cloudflare logs to Sophos XDR:
- HTTP Ingest
- Customer-managed S3
- Sophos-managed S3 (with token)
-
Configure Cloudflare Logpush to send logs to the chosen destination.
- Configure the integration in Sophos XDR.
Requirements
The following is required for Cloudflare SSE configuration:
- A Cloudflare account with Logpush turned on.
- Access to configure Cloudflare Logpush destinations.
Depending on your chosen transport, you also need one of the following:
-
HTTP Ingest:
- Ability to configure an HTTP Logpush destination.
-
Customer-managed S3:
- An AWS account.
- An S3 bucket for Cloudflare logs.
- Permissions to create Lambda, CloudFormation, IAM, and related AWS resources.
-
Sophos-managed S3 (with token):
- Permissions to configure an Amazon S3 destination in Cloudflare.
Add a Cloudflare SSE integration
To integrate Cloudflare SSE, you must first configure a Cloudflare Logpush destination, then configure the integration in Sophos XDR.
Configure Cloudflare Logpush
Choose one of the following transport methods supported by Cloudflare:
Choose this option if your data source supports posting events to a webhook or HTTP endpoint with bearer-token authentication.
To configure Cloudflare log forwarding to a HTTP destination, do as follows:
- In Sophos Fusion, go to Security Operations > Integrations > Marketplace.
-
Click Cloudflare SSE.
The Cloudflare SSE page opens. You can configure integrations here and see a list of any you've already configured.
-
In Configured integrations, click Add new.
- In HTTP Ingest, click Set Up.
-
Enter a name for the integration, then click Done.
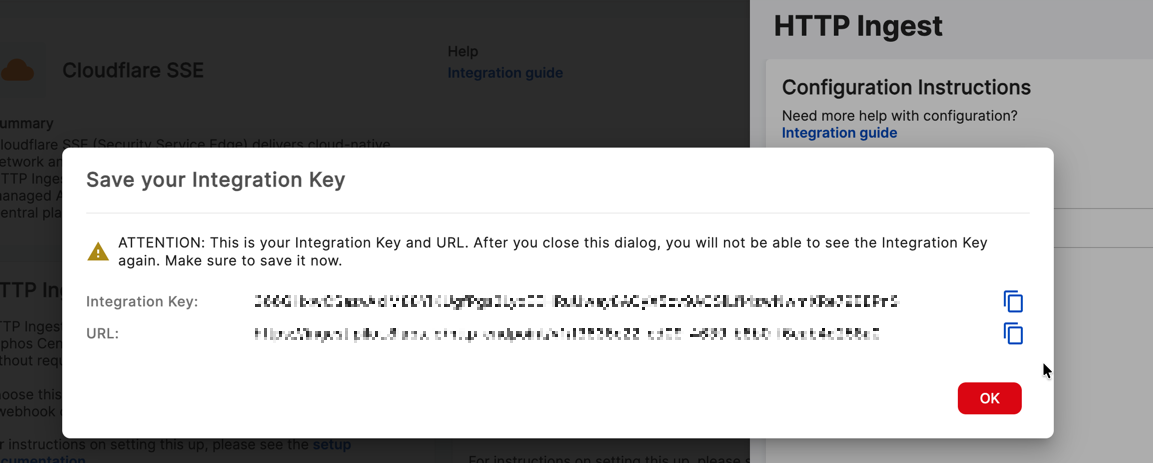
Copy the Integration Key and URL that are displayed.
Copy these values immediately, as they will not be shown again.
-
Follow the steps in Cloudflare's own guide using the Integration Key and URL you saved: Enable HTTP destination.
-
Configure Logpush to send the following fields to Sophos XDR:
Click to view firewall event fields.
ActionClientASNClientASNDescriptionClientCountryClientIPClientIPClassClientRefererHostClientRefererPathClientRefererQueryClientRefererSchemeClientRequestHostClientRequestMethodClientRequestPathClientRequestProtocolClientRequestQueryClientRequestSchemeClientRequestUserAgentDatetimeDescriptionEdgeColoCodeEdgeResponseStatusKindMatchIndexMetadataOriginResponseStatusOriginatorRayIDRayIDRefRuleIDSource
Click to view HTTP requests event fields.
ClientASNClientCountryClientDeviceTypeClientIPClientIPClassClientRequestBytesClientRequestHostClientRequestMethodClientRequestPathClientRequestProtocolClientRequestRefererClientRequestSchemeClientRequestSourceClientRequestURIClientRequestUserAgentClientSrcPortEdgeEndTimestampEdgeStartTimestampEdgeRateLimitActionEdgeRateLimitIDEdgeRequestHostEdgeResponseBytesEdgeResponseContentTypeEdgeResponseStatusEdgeServerIPSecurityActionsSecurityRuleIDsSecuritySourcesOriginIPOriginResponseStatusRayIDRequestHeadersResponseHeadersSecurityActionWAFAttackScoreSecurityRuleIDSecurityRuleDescriptionZoneIDZoneName
Choose this option if your data source writes events to an S3 bucket you control, and you want to keep that bucket in your AWS account.
Create integration in Sophos XDR
To configure Cloudflare log forwarding via your own customer-managed AWS S3 bucket, do as follows:
- In Sophos Fusion, go to Security Operations > Integrations > Marketplace.
-
Click Cloudflare SSE.
The Cloudflare SSE page opens. You can configure integrations here and see a list of any you've already configured.
-
In Configured integrations, click Add new.
- In Customer-managed S3, click Set Up.
- Read the S3 information, then click Next.
-
Enter a name for the integration, then click Done.
A sample AWS CloudFormation (.yaml) template is generated upon completion of the provisioning process. You'll use this when creating a Lambda stack.
Create the Lambda stack
To create the Lambda stack, do as follows:
Note
Complete the deployment in the same AWS region as your Cloudflare SSE logs bucket.
- Log in to the AWS Console for the region (for example,
https://us-east-1.console.aws.amazon.com/cloudformation) with an account that has permissions to create roles, Lambdas, secrets, and policies, or use a role that can assume another role with these permissions. - In the Management and Governance section, select CloudFormation.
-
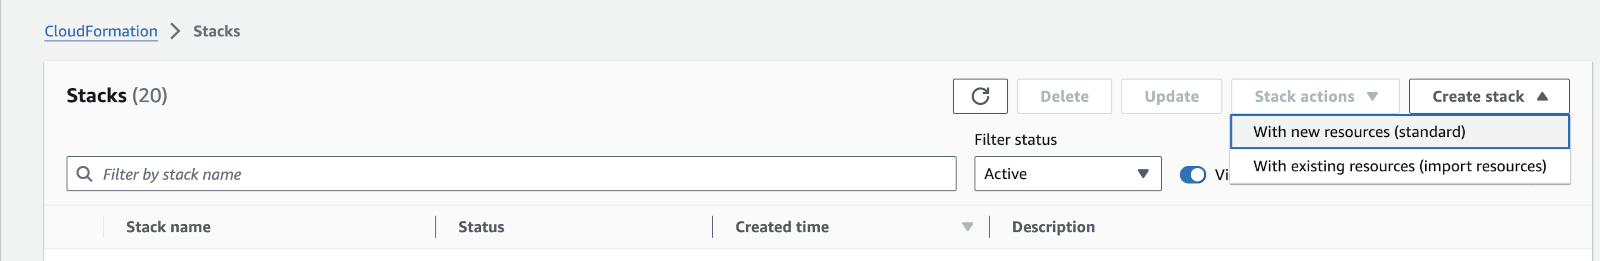
Click Create stack.
Note
You may see a list of CloudFormation stacks when you select CloudFormation. If that's the case, click Create stack > With new resources (standard).
-
In the Prerequisite - Prepare Template section, click Choose an existing template.
- In the Specify Template section, click Upload a template file > Choose file.
-
Upload the downloaded CloudFormation template (.yaml file).
Storing the CloudFormation template in an S3 bucket.
Instead of uploading the template file directly, you can store the CloudFormation template in an S3 bucket and specify the S3 URL when creating the stack.
The bucket doesn't need to be public, versioned, or encrypted, but typically, the template bucket, notification bucket, and Lambda stack should be in the same AWS account and region.
-
Click Next.
-
Enter an appropriate stack name.
Note
Spaces aren't allowed in stack names.
-
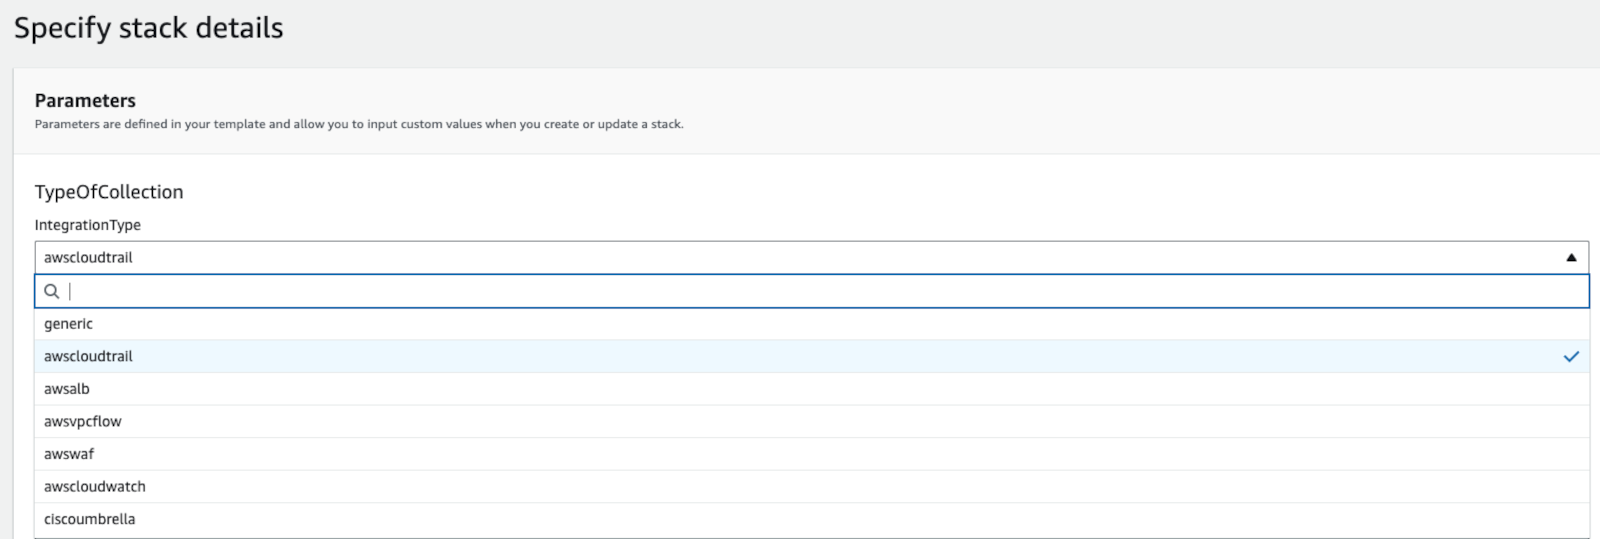
In the IntegrationType drop-down, choose cloudflare.
Note
This field describes what sort of log objects are in the NotificationBucket. If there's more than one type, or you're not sure, choose generic.
-
In NotificationBucket, enter the bucket name (not a URL or URI) that houses the logs.
- (Optional) Enter the appropriate value into SNSNotificationarn if you wish to use SNS notifications going forward instead of S3 notifications.
- Leave the remaining fields as default.
- Click Next.
- Accept the acknowledgment statement: I acknowledge that AWS CloudFormation might create IAM resources.
- Click Next.
- Review all parameters and click Submit.
-
Wait at least 30 seconds, then click Refresh.
The process may take a minute or more to finish. A status of
CREATE_COMPLETEfor the stack indicates the process has finished.
Add the Lambda trigger
Once the Lambda stack is created, add a trigger as follows:
- In the AWS Console, go to the Lambda service.
- Locate the new Lambda by name. The default name is
{STACKNAME}-scwx-tdr-lambda-{INTEGRATIONTYPE}. For example,ct-demo-sophos-xdr-lambda-cloudflare. - Click the Lambda name to open the stack's edit page.
- Expand the Function overview section and click Add Trigger.
-
In the Trigger Configuration editor, select S3 from the drop-down menu.
Optionally, use an SNS trigger configured with a previously created topic.
-
From the Bucket options, find the bucket containing the logs and select it.
- From the Event Type options, choose All Object Create Events.
- In the Prefix field, enter the bucket prefix where the logs are located. Leave this blank if no prefix is used.
- Leave the Suffix field blank.
- Accept the acknowledgment statement about the cost impact of a Lambda function.
-
Click Add.
The configuration page for that Lambda displays again. A message at the top indicates that the trigger was added successfully. For example,
The trigger wmikeking was successfully added to function Logs-XDR-Upload.The function is now receiving events from the trigger.
Choose this option if your data source vendor requires an ownership challenge token to be sent to the S3 destination as proof of bucket ownership.
Create integration in Sophos XDR
To configure Cloudflare log forwarding to a Sophos-managed AWS S3 bucket, do as follows:
- In Sophos Fusion, go to Security Operations > Integrations > Marketplace.
-
Click Cloudflare SSE.
The Cloudflare SSE page opens. You can configure integrations here and see a list of any you've already configured.
-
In Configured integrations, click Add new.
- In S3 Ingest - Sophos-Managed (with token), click Set Up.
- Choose the IAM User authentication type.
- Enter a name for the integration
-
For IAM User, enter the following:
arn:aws:iam::391854517948:user/cloudflare-logpush -
Click Done.
The integration is created and the Configured Integrations table is shown.
-
Click the integration's name to open it.
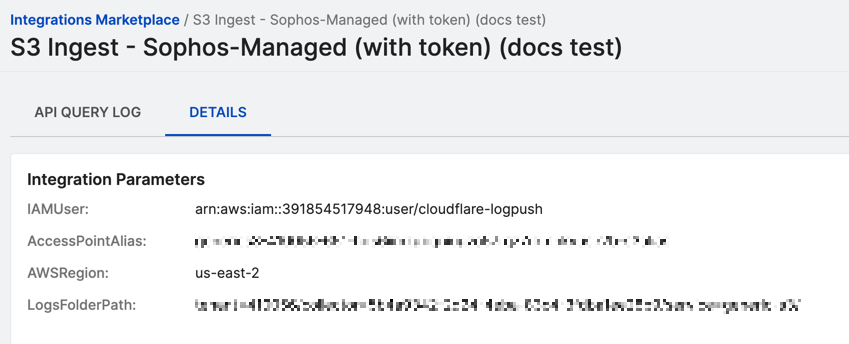
- Click the Details tab.
-
Note the following integration parameters listed in this tab:
AccessPointAliasAWSRegionLogsFolderPath
You need these for configuring log forwarding in Cloudflare.
Configure log forwarding
- Follow the steps in Cloudflare's own guide: Enable Amazon S3.
-
Configure the following parameters:
- Bucket: Enter the
AccessPointAliasvalue you got from Sophos XDR. - Path: Enter the
LogsFolderPathvalue you got from Sophos XDR. - Organize logs into daily subfolders: Turn on.
- My policy requires AWS SSE-S3 AES256 Server Side Encryption: Turn on.
- Bucket: Enter the
-
Cloudflare will send a file to your designated destination to prove S3 bucket ownership.
Reload the integration's Details tab in Sophos XDR and copy the new
OwnershipTokenvalue. -
Enter the token in the Cloudflare dashboard to verify your access to the S3 bucket.
The new integration appears under Configured integrations. If its status icon is a green tick, your data should appear in the Sophos Data Lake after validation.
Additional resources
For more information on configuring Cloudflare SSE, see the following documents: