Hotfix: Security updates
Sophos Firewall offers hotfixes, a unique capability that patches and protects the running system without requiring a firmware upgrade. Hotfixes help protect the firewall against vulnerabilities identified in security advisories and deliver other required fixes.
Hotfix security updates show the hotfixes applied to the current SFOS version to address vulnerabilities and other security issues.
These updates are specific to each SFOS version and appear on Backup & firmware > Hotfix: Security updates.
Learn about hotfix requirements, behavior, notifications and logs, and frequently asked questions.
Requirement
The firewall applies hotfixes and lists the related security updates when the hotfix setting is turned on in the CLI. It's on by default.
We recommend that you keep the hotfix setting on to make sure the firewall receives security updates.
To verify the status, see hotfix commands.
Notifications and logs
The firewall supports email notifications, logs, and audit logs only for hotfix security updates.
-
To turn on email notifications, do as follows:
- Go to System services > Notification list.
- Under Firmware, select Email for Security updates.
-
SNMP notifications aren't available for these updates.
- You can see these updates in Log viewer.
- Audit logs of these updates are generated and forwarded to Sophos Fusion for use in Central Firewall Reporting. See Audit logs.
Behavior
Learn how hotfix security updates relate to SFOS versions and how the firewall applies them.
- More than one hotfix may be required to fully protect against a vulnerability. So, some vulnerabilities appear more than once on the list.
- When you upgrade to a different SFOS version, the previous version's hotfix list is removed, and the new version's list is shown. The page remains empty if no hotfix security updates have been applied to the new version.
- When you upgrade, the firewall installs the new version and then applies any hotfixes available for that version.
-
You can sort hotfix security updates by the date they were applied.
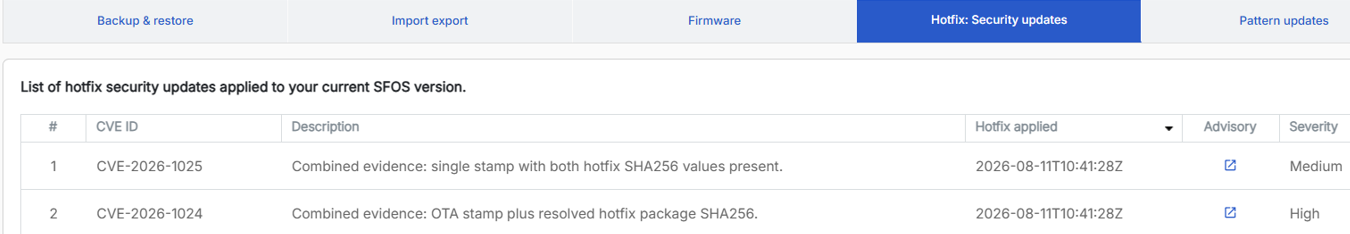
-
Most hotfix security updates address publicly disclosed vulnerabilities. The Advisory column includes a link to the relevant Sophos security advisory. However, some hotfixes address internal issues and don't include either a CVE ID or an advisory link.
FAQs
Do hotfixes require the firewall to restart?
No. Hotfixes are designed not to restart the firewall. The firewall installs them silently and without affecting performance.
How are hotfixes decided?
Hotfixes are reserved for security vulnerabilities and issues that can affect many organizations, so they aren't released frequently. When determining whether an issue is suitable for a hotfix, its potential impact on network traffic and performance is considered. As a result, hotfixes are designed to address issues without disrupting normal network operations.
Do maintenance versions have hotfixes?
Yes.
Why don't I see any hotfixes on the Hotfix page? Or why do the same hotfixes appear after a firmware upgrade?
The page shows the hotfix security updates installed since the firewall was upgraded to the current SFOS version. Although hotfixes are specific to each SFOS version, the same hotfix may be independently applied to multiple versions.
After an upgrade, the page appears as follows:
- If the new version already has the fixes from the previous version built into its firmware, the page may be empty or show only hotfixes specific to the new version.
- If the new version has one or more hotfixes in common with the previous version, those hotfixes may appear on the page because they've been applied independently to the new version.
How are hotfixes applied to a high-availability cluster?
Hotfixes are applied to the current primary device. The primary device then synchronizes with the auxiliary device, and the hotfix is applied to the auxiliary device.