Add a Web Application Firewall (WAF) rule
With WAF rules, you can control how traffic is handled for published web applications. For each path within a domain, you can block requests, protect applications with WAF, return a redirect response, or pass traffic directly to a backend server. The firewall handles matching traffic according to the action you specify.
You configure a WAF rule for an IP address assigned to a network interface, port, and one or more domain names. The firewall matches traffic based on the IP address assigned to the interface.
For HTTPS traffic, it uses Server Name Indication (SNI) to determine the server that corresponds to the hostname in the client request.
Restriction
You can create a maximum of 60 WAF rules. See WAF limitation.
WAF doesn't support WebDAV, so applications such as Nextcloud aren't supported. We recommend that you route such traffic through firewall rules instead of WAF rules.
To add a WAF rule, do as follows:
- Go to Rules and policies > Firewall, select IPv4, click Add firewall rule, then select New firewall rule.
- Rules are turned on by default. You can turn off a rule if you don’t want to apply its matching criteria.
General details
Enter the general details.
| Setting | Description |
|---|---|
| Rule name | Enter a name. |
| Rule position | Specify the position of the rule. Available options:
|
| Rule group | Specify the rule group to which you want to add the firewall rule. You can also create a new rule group by using Create new from the list. If you select Automatic, the firewall rule is added to an existing group based on the first match with the rule type and source-destination zones. |
| Action | Select Protect with web server protection. |
| Preconfigured template | Select a template to apply:
When you select a template, the firewall automatically creates the necessary paths under Traffic routing with the Action set to Protect. You must edit the paths to add web servers to them. You can also change the other settings according to your requirements. |
Hosted server
Enter the Hosted server details.
| Setting | Description |
|---|---|
| Hosted address | Select the public IP address assigned to an interface through which users access the internal server or host. The WAF rule is bound to the IP address assigned to the interface. You can use the public IP address assigned to the interface or use an alias to bind the required public IP address. When a client establishes a connection and accesses the web server, the web server obtains the interface address configured in the WAF rule. The HTTP header |
| Listening port | Enter the port number on which to reach the hosted web server. The defaults are port 80 for HTTP and port 443 for HTTPS. Make sure WAF is different in at least one of the following attributes from the VPN portal and SSL VPN: WAN IP address, port, protocol. See Port sharing among services. You can't use some ports as these are reserved by the firewall for system services. For details, see Reserved ports. |
| HTTPS | If you turn this on, the hosted server is accessible through HTTPS and not through HTTP. |
| HTTPS certificate | If you selected HTTPS, select the certificate. The certificate name can only contain alphanumeric characters from the US ASCII character set. The domains of the selected certificate automatically appear under Domains and overwrite the existing ones. The firewall supports SNI (Server Name Indication), allowing you to create more than one virtual web server that's accessible over the same IP address and port. You can assign a different certificate to each server. Servers are presented to clients based on the requested hostname. To create or upload a certificate, go to Certificates > Certificates. |
| Redirect HTTP | Select to redirect port 80 traffic to port 443. |
| Domains | Enter the FQDN configured for the web server, for example, Don't use underscores ( If you've turned on HTTPS, domain names of the selected HTTPS certificate show in the list. You can edit or delete these or add new domain names. You can use the wildcard Example: A single WAF policy supports multiple wildcard domains. Virtual web servers with wildcard domains are only matched when there are no virtual web servers with specific domains configured. Example: A client request to the domain, When you add a subdomain to Domains and then try and access another subdomain under the same domain, the firewall won't generate a block page. Instead, you'll get a valid HTTP response code. You can see this in the reverse proxy logs. Example: If you add |
Traffic routing
Traffic routing lets you define how the firewall handles traffic for each path in a WAF rule. Each WAF rule includes a default path that you can edit. You can also add additional paths and configure a traffic routing action for each path.
Default path
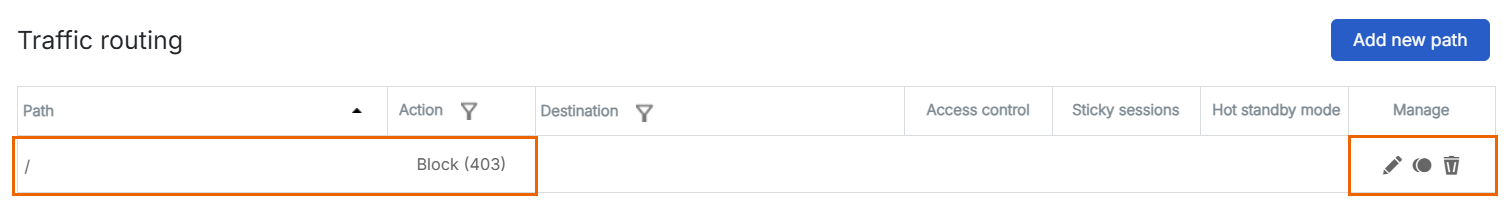
By default, each WAF rule includes the root path / with the action set to Block. This blocks requests to all paths until you configure additional traffic routing actions.
Click Edit  to add paths and change the action. You can change the action to Protect, Redirect, or Passthrough. Alternatively, leave it as Block and add more specific paths that use different actions. Requests that don't match a specific path use the default path.
You can edit, clone, or delete the default path.
Add new path
You can add new paths to route traffic based on the action you specify for those paths.
Options depend on the action you want to specify.
To see the available options for your action, click the appropriate tab below.
Add the paths that you want to block. Requests that match the path are blocked immediately and aren't forwarded to a backend web server.
To add a path with the Block action, do as follows:
- Click Add new path.
-
Specify the following settings:
Setting Description Paths Specify one or more paths that you want to block. Action Select Block. Response code Select the response code that you want to return from the following options:
- Bad Request (400): Blocks access to invalid requests.
- Unauthorized (401): Requires valid authentication credentials to access the requested content.
- Payment Required (402): Indicates that payment is required to access the requested content.
- Forbidden (403): Blocks access to the requested resource.
- Resource Not Found (404): Indicates that the requested content could not be found.
- Method Not Allowed (405): Indicates that the requested content doesn't support the requested method.
- Not Acceptable (406): Indicates that the requested format isn't available.
- Proxy Authentication Required (407): Indicates that authentication with a proxy server is required to access the requested content.
- Request Timeout (408): Indicates that the request timed out before it was completed.
- Conflict (409): Indicates that there's a conflict with the current state of the requested content.
- Resource Unavailable (410): Indicates that the requested content is no longer available.
- Length Required (411): Indicates that the length of the request must be specified before the request can be processed.
- Precondition Failed (412): Indicates that the required conditions aren't met to process the request.
- Request Entity Too Large (413): Indicates that the request could not be processed because the request content is too large.
- Request URL Too Long (414): Indicates that the request could not be processed because the URL is too long.
- Unsupported Media Type (415): Indicates that the request could not be processed because the content format isn't supported.
- Requested Range Not Satisfiable (416): Indicates that the requested content is outside the available range.
- Expectation Failed (417): Indicates that the requirements specified in the request could not be met.
- Unprocessable Entity (422): Indicates that the request could not be processed because it contains errors.
- Locked (423): Indicates that the requested content could not be modified because it's locked.
- Failed Dependency (424): Indicates that the request could not be processed because a dependent request failed.
- Upgrade Required (426): Indicates that a different protocol is required to process the request.
For more information about response codes, see Client Error 4xx.
-
Click Save.
Add paths that you want to protect using WAF. Requests that match the path are forwarded to the selected web server and inspected according to the settings you specify. You can specify multiple web servers, an authentication method, and allowed and blocked client networks. You can also bind sessions to servers and specify primary and backup servers.
Note
If you select multiple web servers, requests are balanced among the web servers.
To add a path with the Protect action, do as follows:
- Click Add new path.
-
Specify the following settings:
Setting Description Paths Specify one or more paths that you want to protect. Action Select Protect. Web server Select the web servers from the Web server list. Alternatively, you can create new ones. You can see the selected web servers under Selected web servers. Authentication Specify an authentication profile for web applications. Allowed client networks Specify the IP addresses and networks that can connect to the hosted web server.
The default value is Any IPv4. Keep the default value if you don't want to restrict access to specific IP addresses or networks. If you leave this setting blank, the WAF rule won't work, and the browser shows a "400 Bad Request" error.
Blocked client networks Specify the IP addresses and networks to block from connecting to the hosted web server. Blocked countries Specify the countries or country groups you want to block from connecting to the hosted web server. Block IP addresses of unknown country-origin Turn on to block IP addresses whose country of origin is unknown.
Use caution when turning this on because you might be unable to access the web application if you're connecting from an IP address with an unknown country origin. You can check if your IP address has a country-origin or not. See GeoIP2 Databases Demo.
Sticky session cookie Turn it on to bind a session to a web server. The firewall forwards a cookie to the user's browser, enabling it to route requests from the browser to the same web server.
If the server isn't available, the cookie is updated, and the session is switched to another web server.
Hot-standby mode Turn it on to send all requests to the first selected web server. The other web servers remain as backup servers and are used if the first server fails.
When the main server starts functioning again, the sessions are switched back to it. If you select Sticky session cookie, the session continues with the backup web server.
-
Click Save.
Add a passthrough path to forward requests for specific paths directly to a backend web server without WAF inspection. Passthrough creates a tunnel through WAF and is typically used for WebSocket traffic. Protection policies don't apply to passthrough paths.
Note
The firewall doesn't evaluate requests based on the order of path listing. It applies the paths, starting with the longest path and ending with the default path route. The default path is used only if a more specific path doesn't match the request.
To add a path with the Passthrough action, do as follows:
- Click Add new path.
-
Specify the following settings:
Setting Description Paths Specify one or more paths whose requests you want to route through a WebSocket tunnel. Action Select Passthrough. Web server Select the web servers from the Web server list. Alternatively, you can create new ones. You can see the selected web servers under Selected web servers. Authentication Specify an authentication profile for web applications. Allowed client networks Specify the IP addresses and networks that can connect to the hosted web server. The firewall only implements the protection for IP host type IP and Network. Don't specify an IP range or IP list. Blocked client networks Specify the IP addresses and networks to block from connecting to the hosted web server.
The firewall only implements the protection for IP host type IP and Network. Don't specify an IP range or IP list.
Blocked countries Specify the countries or country groups you want to block from connecting to the hosted web server. Block IP addresses of unknown country-origin Turn on to block IP addresses whose country of origin is unknown.
Use caution when turning this on because you might get blocked from this resource if you're connecting from an IP address of unknown country-origin. You can check if your IP address has a country-origin or not. See GeoIP2 Databases Demo.
Sticky session cookie Turn it on to bind a session to a web server. The firewall forwards a cookie to the user's browser, enabling it to route requests from the browser to the same web server.
If the server isn't available, the cookie is updated, and the session is switched to another web server.
Hot-standby mode Turn it on to send all requests to the first selected web server. The other web servers remain as backup servers and are used if the first server fails.
When the main server starts functioning again, the sessions are switched back to it. If you select Sticky session cookie, the session continues with the backup web server.
-
Click Save.
Add a redirect path to return an HTTP redirection response for specific paths. The response includes a destination URL that the client can follow. This path lets you use multiple domain names for your websites, shorten URLs, and prevent broken links after a website is moved. For example, if your organization changes its name and uses a new URL, visitors can reach the new website when they enter the old URL.
The firewall doesn't inspect redirect requests and doesn't forward them to a backend web server.
To add a redirect path, do as follows:
- Click Add new path.
-
Specify the following settings:
Setting Description Paths Specify one or more paths that you want to redirect. Action Select Redirect. Response code Select the response code that you want to return from the following options:
- Multiple Choices (300): Indicates that multiple responses are available for the requested resource.
- Resource Moved Permanently (301): Redirects incoming requests for a permanently moved path to a new one.
- Resource Moved Temporarily (302): Redirects incoming requests for a temporarily moved path to an alternative one.
- See Another Resource (303): Redirects to a different path to get the requested information.
- Resource Not Modified (304): Indicates that the requested resource hasn't changed since the last request and that the client can use its cached copy.
- Use Proxy (305): Uses a proxy server to access the requested content.
Caution: This code is deprecated because of security concerns. We recommend that you use it only for internal resources.
- Temporary Redirection (307): Redirects to a different path temporarily while using the same request method.
- Permanent Redirect (308): Redirects permanently to a different path while using the same request method.
For more information about the status codes, see Redirection 3xx.
Protocol Select whether to use HTTP or HTTPS to connect to the host. Host Select the new FQDN host to which you want to redirect the request. Path Enter the new path to which you want to redirect the request. Port Enter the port number used to connect to the destination host. For HTTP, the default port is 80. For HTTPS, the default port is 443. -
Click Save.
Exceptions
Select Add new exception to specify the security checks to skip.
Select the paths, sources, categories, and security checks to skip. For more information about categories, see the Common threat filter settings in Add a protection policy.
You can specify more than one exception in a WAF rule.
| Setting | Description |
|---|---|
| Paths | Specify the paths for which you want to create an exception. The path is case-sensitive. You can use wildcards in the paths. Example: |
| Operation | Select the Boolean operation for paths and source networks. |
| Sources | Specify the IP addresses, range, list, or networks from which the traffic originates. |
| Cookie signing | Skips check for cookie tampering. Cookie signing mitigates attempts to obtain private session data and engage in fraudulent activity by tampering with cookies. When the web server sets a cookie, a second cookie is added to the first cookie containing a hash built from the primary cookie's name and value and a secret known only to the firewall. If a request can't provide the correct cookie pair, the cookie is dropped. |
| Static URL hardening | Allows rewritten links for the specified paths and source networks. Static URL hardening prevents users from manually constructing deep links that lead to unauthorized access. When a client requests a website, all static URLs of the website are signed using a procedure similar to cookie signing. In addition, the response from the web server is analyzed regarding which links can be validly requested next. When you turn on static URL hardening, the entries for URL paths become case-sensitive. For example, if you add the path |
| Form hardening | Skips checks for web form rewriting. To prevent tampering with forms, the firewall saves the original structure of a web form and signs it. If the structure has changed when the form is submitted, the firewall rejects the request. |
| Antivirus | Skips anti-virus scanning for requests from the specified source networks and to the paths that you specify. |
| Block clients with bad reputation | Skips checks for clients that have a bad reputation according to real-time blackhole lists (RBLs) and GeoIP information. |
| Never change HTML during static URL hardening or form hardening | If you select this exception, the firewall doesn't perform an HTML rewrite during static URL hardening or form hardening. For example, it doesn't update the links inside an HTML page and retains the full link returned by the web server. You may have to skip static URL hardening or form hardening to allow access to these links. So, if a web application needs anything in the HTML page to function, it isn't dropped by HTML rewrite. |
| Accept unhardened form data | Even if you select the Form hardening exception, the firewall doesn't accept form data if the form hardening signature is missing. With this option, the firewall accepts unhardened form data. |
Advanced
Specify the advanced protection policies and settings as follows:
-
Specify the advanced protection policies.
Setting Description Protection Specify a protection policy for the servers. Protection policies apply only to paths whose Action is set to Protect under Traffic routing. Intrusion prevention Specify an intrusion prevention policy.
The communication protocol between the firewall and the web server must be HTTP to use intrusion prevention with WAF.
Traffic shaping Specify a traffic shaping policy to allocate bandwidth. -
Specify the Advanced settings.
Setting Description Disable compression support When clients request compressed data, the firewall sends data in compressed form.
Select this setting to turn off compression if web pages appear incorrectly or if users experience content-encoding errors. The firewall then requests uncompressed data from web servers and sends it to the client irrespective of the request’s encoding parameter.
Rewrite HTML Select to rewrite the links of returned web pages to retain link validity.
Example: If a web server's hostname is
yourcompany.local, but the hosted web server’s hostname isyourcompany.com, absolute links like[a href="http://yourcompany.local/"]are broken if the link is not rewritten to[a href="http://yourcompany.com/"]before delivery to the client.You don't need to select this option if
yourcompany.comis configured on your web server or if internal links on your web pages are always realized as relative links.We recommend that you use the option with Microsoft Outlook web access or SharePoint portal server.
HTML rewriting affects all files with HTTP content type text/* or *xml*. * is a wildcard. To prevent corruption during HTML rewriting, make sure that other file types (example: binary files) have the correct HTTP content type.
Rewrite cookies Select to rewrite cookies of the returned web pages. Pass host header Select to forward the host header requested by the client to the web server.
You can use this to match the requested hostname with the web server when you've hosted more than one website on a server.
-
Click Save. When you save a WAF rule, the firewall restarts all web server protection rules. Live connections using any of these rules will be lost and need to be re-established.
You can see the WAF rule you created in the Firewall rules table.